|
The Daily Reconcile.
All the cloud native news that’s fit to reconcile
| Thursday, November 5, 2026 |
Two pages |
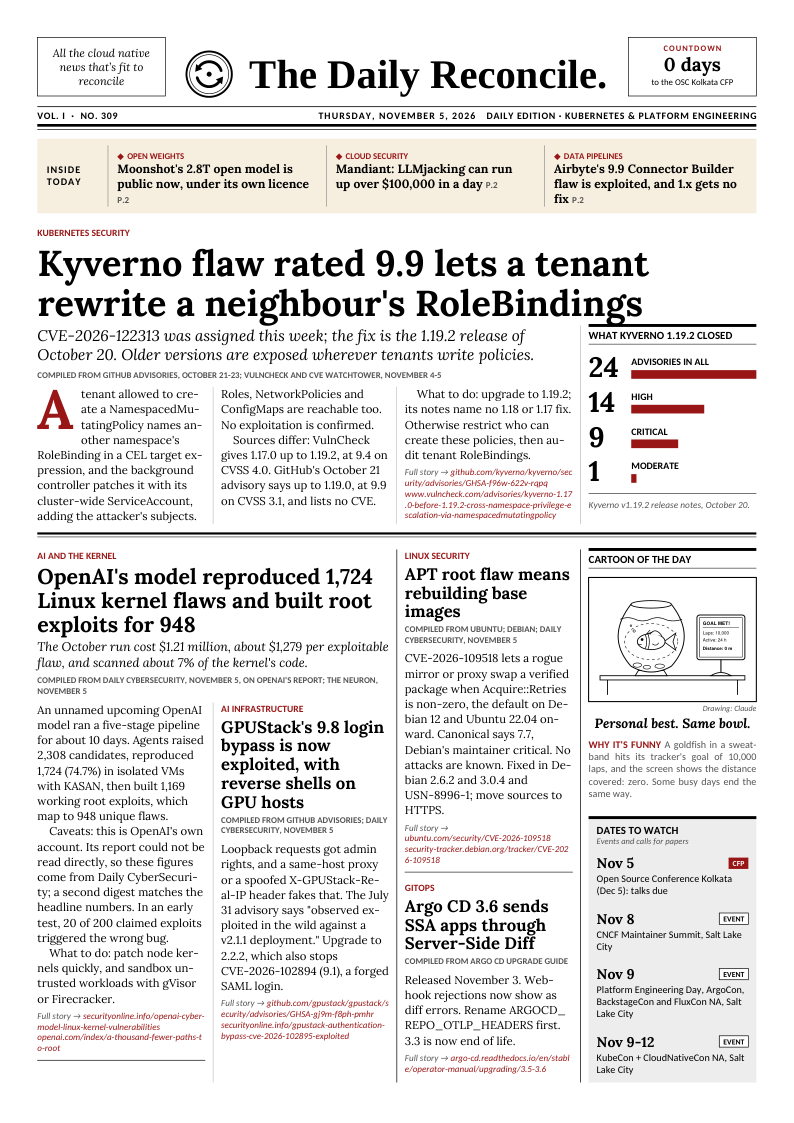
Front page · tap to read the PDF
Kubernetes security
Kyverno's CVE-2026-122313, rated 9.9 on CVSS 3.1, lets a tenant allowed to create a NamespacedMutatingPolicy rewrite another namespace's RoleBindings through the background controller. The fix is 1.19.2 from October 20, which closes 24 advisories, 9 of them critical. Its notes name no 1.18 or 1.17 fix, and sources differ on the affected range.
What Kyverno 1.19.2 closed | Advisories in all | | 24 | | High | | 14 | | Critical | | 9 | | Moderate | | 1 |
Bars to one scale, highest value 24 |
Also in today’s two pages
| → | OpenAI says an upcoming model reproduced 1,724 Linux kernel flaws and built root exploits for 948, for $1.21 million. | | → | GPUStack's 9.8 login bypass is exploited, with reverse shells on GPU hosts. Upgrade to 2.2.2. | | → | APT's CVE-2026-109518 gives root over HTTP: patch, then rebuild base images. | | → | Argo CD 3.6 moves Server-Side Apply apps to Server-Side Diff. | | → | Krateo PlatformOps: authn and frontend add PKCE, and snowplow 1.12.65 fixes a cache deadlock. |
| | kubectl tip kubectl logs deploy/my-deployment shows Pod logs for a Deployment. |
|
Want it on paper?
The PDF is laid out for exactly this: A4, two pages, printed on one sheet. It is how this paper is read every morning.
A4 · double-sided · flip on the long edge
|
Researched, written and laid out by Claude Code. Every item links to its source; always check the original.
Made by Diego Braga, who decides what it covers.
Sources today: Daily CyberSecurity, GitHub, VulnCheck, Debian, Ubuntu, CNCF, InfoQ, Hugging Face, TechNode
You get this because you asked for it, and for nothing else. We keep your address and your paper preference, and no other data.
Privacy ·
Source on GitHub
|