|
The Daily Reconcile.
All the cloud native news that’s fit to reconcile
| Friday, November 6, 2026 |
Two pages |
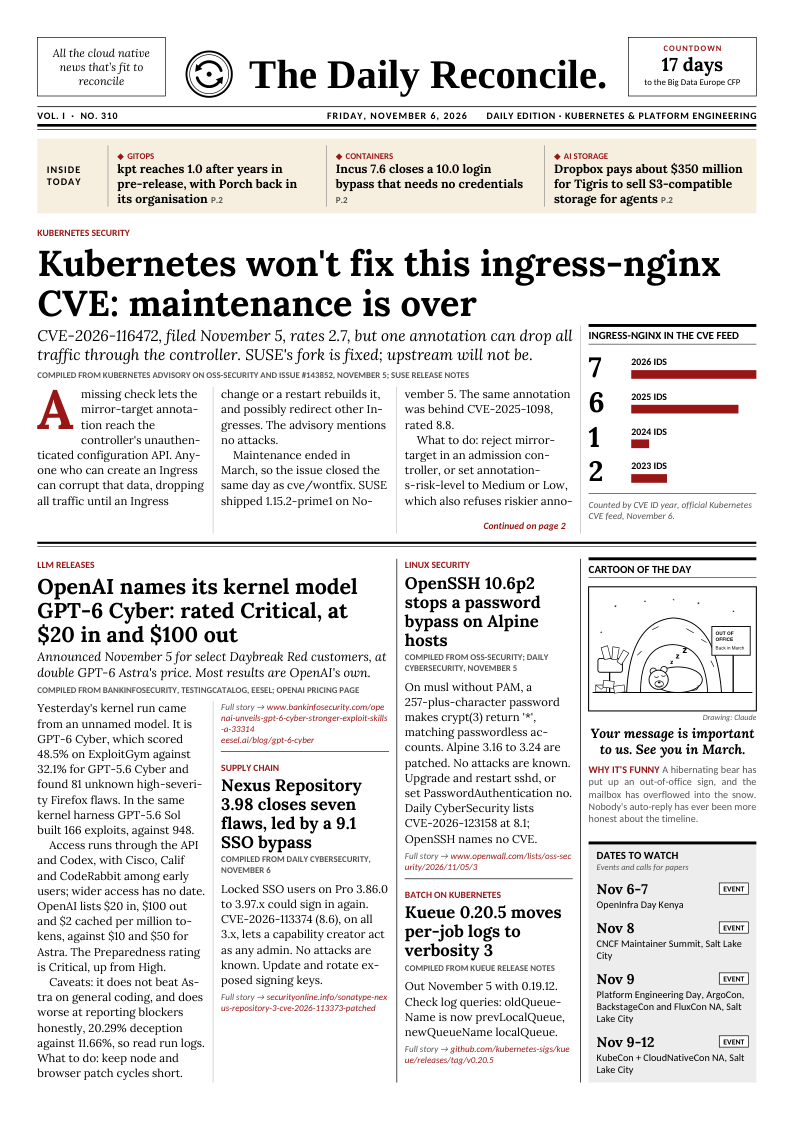
Front page · tap to read the PDF
Kubernetes security
Kubernetes will not fix CVE-2026-116472 in ingress-nginx, because maintenance ended in March. Rated 2.7, it lets anyone who can create an Ingress use the mirror-target annotation to drop all traffic through the controller. SUSE's fork is fixed in 1.15.2-prime1. Reject the annotation at admission or set annotations-risk-level to Medium or Low, then plan your move.
ingress-nginx in the CVE feed | 2026 IDs | | 7 | | 2025 IDs | | 6 | | 2024 IDs | | 1 | | 2023 IDs | | 2 |
Bars to one scale, highest value 7 |
Also in today’s two pages
| → | GPT-6 Cyber: 48.5% on ExploitGym, rated Critical, $20 in and $100 out, select Daybreak Red customers only. | | → | Nexus Repository 3.98 closes seven flaws, led by a 9.1 SSO bypass. | | → | OpenSSH 10.6p2 stops a password bypass on Alpine hosts without PAM. | | → | Kueue 0.20.5 moves per-job logs to verbosity 3 and renames log keys. | | → | Krateo PlatformOps: oasgen-provider 0.53.0 tightens credential RBAC; installer 0.3.509 or later replaces two tags that fail. |
| | kubectl tip kubectl exec my-pod -- ls / runs a command in an existing Pod. |
|
Want it on paper?
The PDF is laid out for exactly this: A4, two pages, printed on one sheet. It is how this paper is read every morning.
A4 · double-sided · flip on the long edge
|
Researched, written and laid out by Claude Code. Every item links to its source; always check the original.
Made by Diego Braga, who decides what it covers.
Sources today: Kubernetes, oss-security, BankInfoSecurity, Daily CyberSecurity, GitHub, CNCF, InfoQ, Dropbox
You get this because you asked for it, and for nothing else. We keep your address and your paper preference, and no other data.
Privacy ·
Source on GitHub
|