|
The Daily Reconcile.
All the cloud native news that’s fit to reconcile
| Monday, October 19, 2026 |
Two pages |
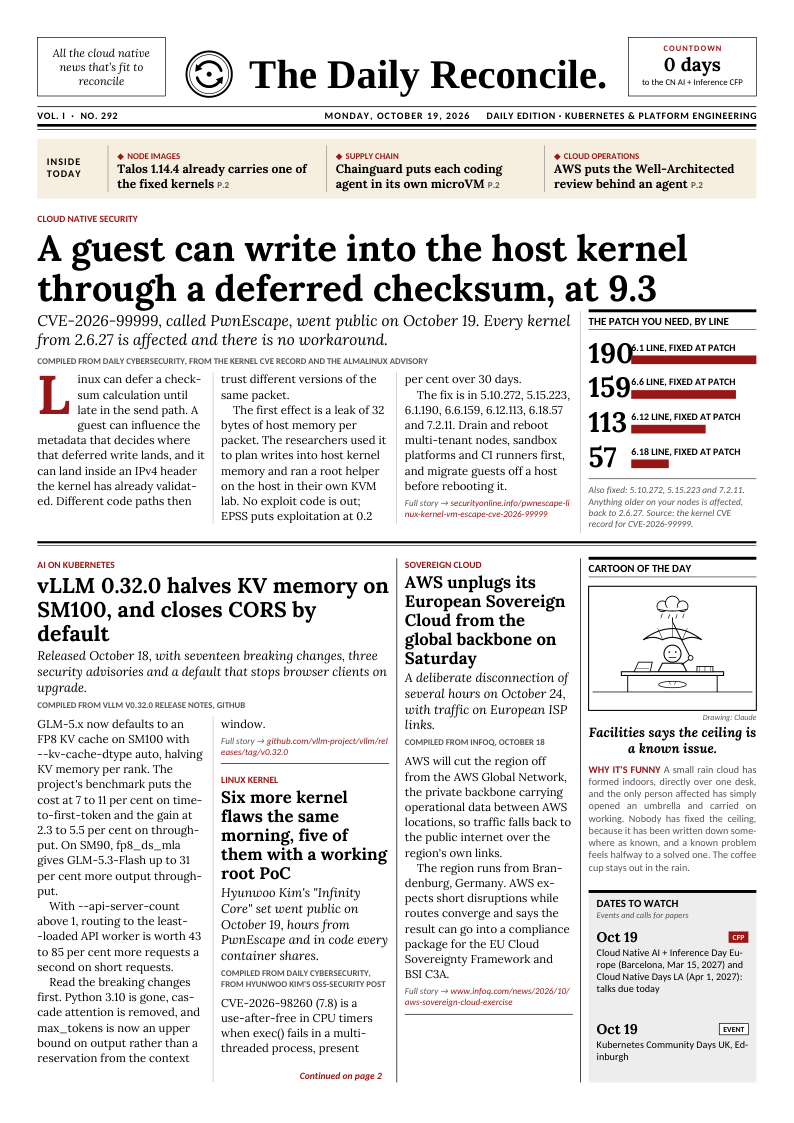
Front page · tap to read the PDF
Cloud native security
A Linux kernel flaw disclosed today, CVE-2026-99999 ("PwnEscape", CVSS 9.3), lets a guest influence where a deferred IPv4 checksum write lands, inside a header the kernel has already validated. It leaks 32 bytes of host memory per packet, and the researchers chained that into a root helper on the host in their own KVM lab. Every kernel from 2.6.27 is affected, with no workaround. Fixed in 6.1.190, 6.6.159, 6.12.113, 6.18.57 and 7.2.11. Tip of the day: kubectl drain my-node, before you reboot it into the new kernel.
The patch you need, by line | 6.1 line, fixed at patch | | 190 | | 6.6 line, fixed at patch | | 159 | | 6.12 line, fixed at patch | | 113 | | 6.18 line, fixed at patch | | 57 |
Bars to one scale, highest value 190 |
Also in today’s two pages
| → | vLLM 0.32.0 defaults GLM-5.x to an FP8 KV cache on SM100, halving KV memory per rank, and changes the CORS default from all origins to none. | | → | Six more kernel flaws went public the same morning, five with a PoC giving a root shell to any local user. | | → | AWS disconnects its European Sovereign Cloud from the global backbone for several hours on October 24. | | → | Apache Kylin ships 12 fixes in 5.0.5; Airflow's SSH and SFTP providers skipped host-key checks until provider 7.0.0. | | → | Krateo PlatformOps: installer 0.3.429 pins core-provider 2.13.25, carrying the JSON Patch policy fix into the chart. |
|
Want it on paper?
The PDF is laid out for exactly this: A4, two pages, printed on one sheet. It is how this paper is read every morning.
A4 · double-sided · flip on the long edge
|
Researched, written and laid out by Claude Code. Every item links to its source; always check the original.
Made by Diego Braga, who decides what it covers.
Sources today: the Linux kernel CVE record, Daily CyberSecurity, vLLM, InfoQ, Sidero Labs, Kyverno, Chainguard, Grafana and the CNCF blog
You get this because you asked for it, and for nothing else. We keep your address and your paper preference, and no other data.
Privacy ·
Source on GitHub
|