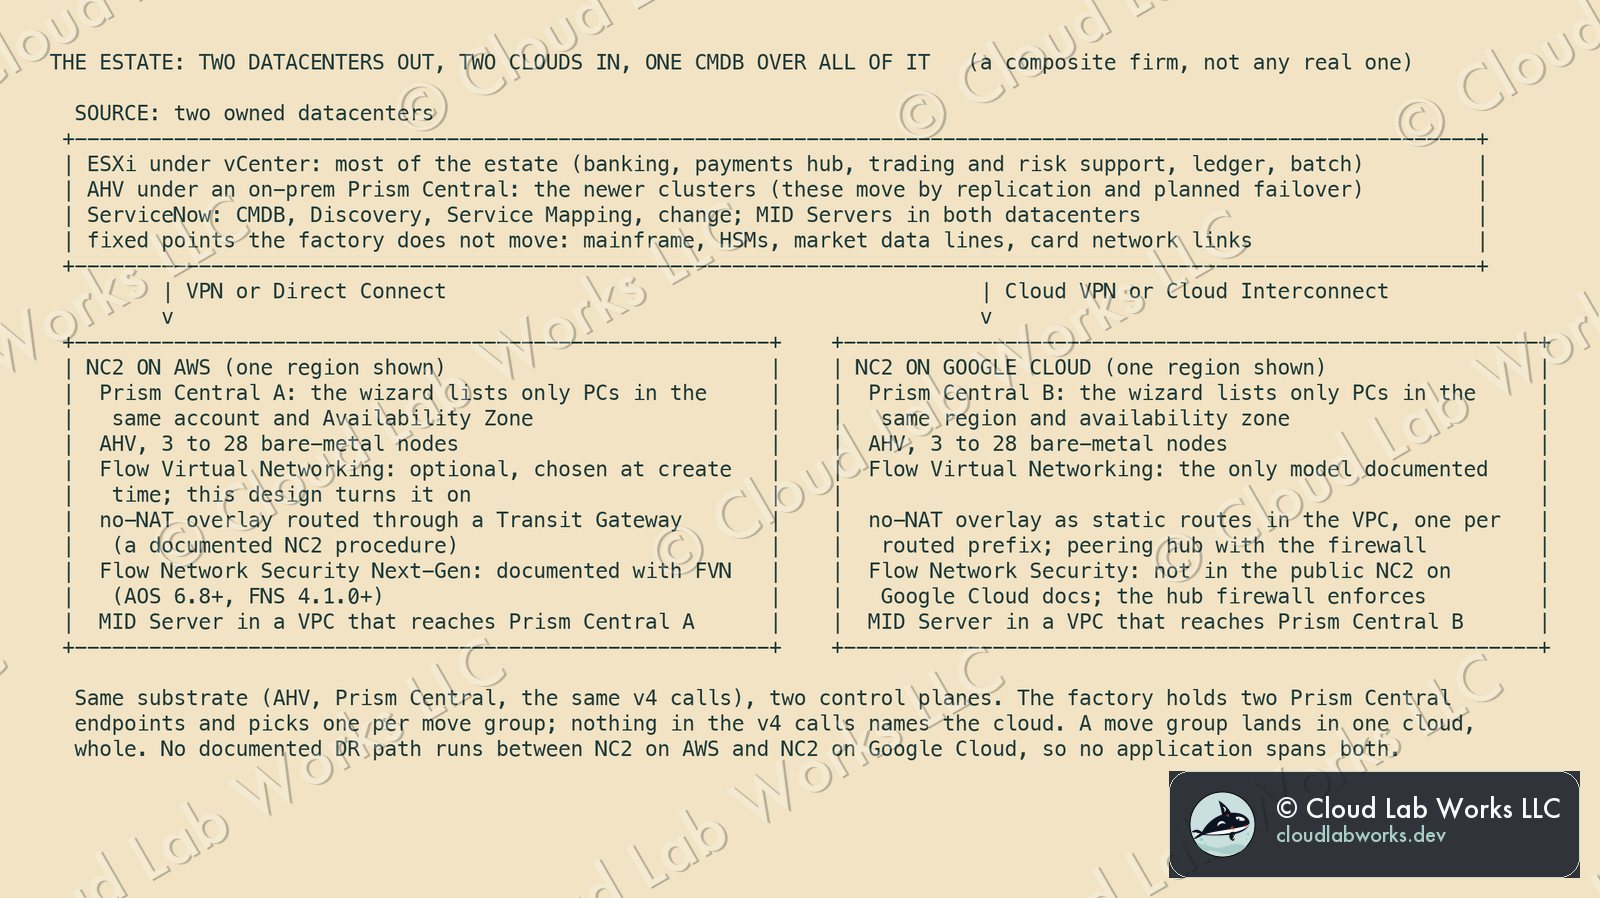
A migration factory on two clouds: ServiceNow CMDB and the Nutanix v4 API, moving a financial services estate onto NC2 on AWS and Google Cloud
A composite large financial services firm (banking, payments, capital markets) leaves two datacenters for NC2 on AWS and NC2 on Google Cloud, and runs it as a factory, not a project: eight stages, each a ServiceNow record, with the platform work done through the Nutanix v4 APIs and Nutanix Move's own API. Categories are the key the CMDB and Prism Central share, the dependency map becomes the Flow Network Security policy, wave patterns graduate from normal to standard change, and month-end freezes become blackout windows. Eight diagrams, every endpoint from the published specs, the FFIEC, NYDFS, DORA and third-party guidance quoted from source, and the parts of the ask the docs don't support marked as such.
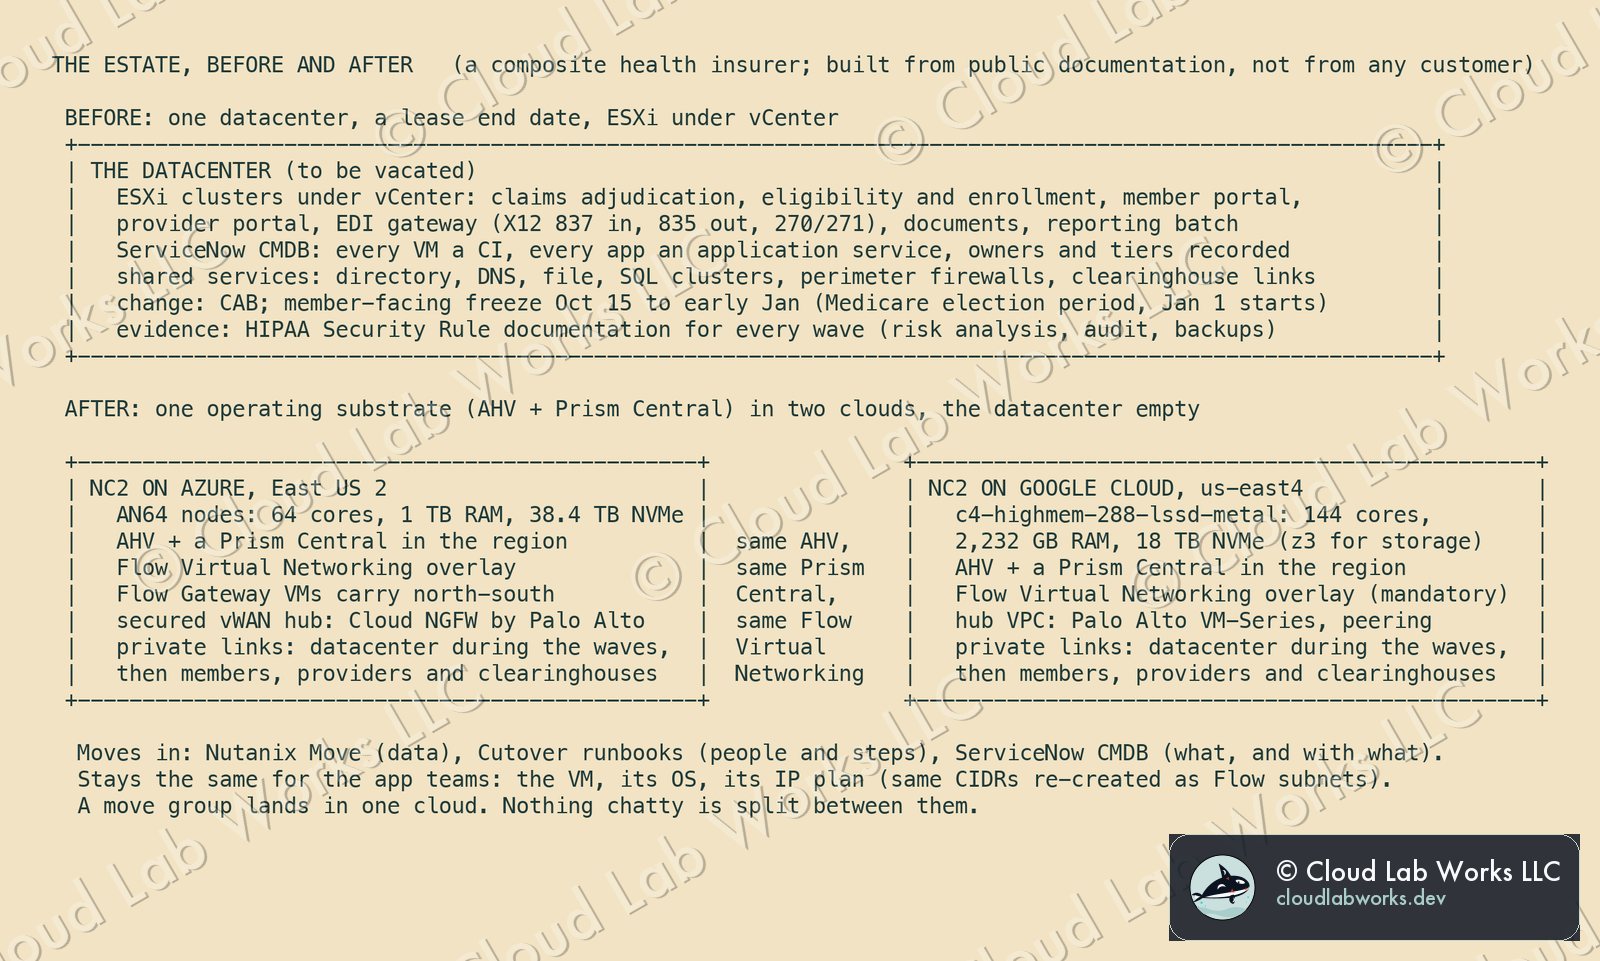
One substrate, two clouds: leaving an ESXi datacenter for NC2 on Azure and Google Cloud
A composite large health insurer has to vacate an ESXi datacenter and lands on NC2 on Azure and NC2 on Google Cloud, with AHV and Prism Central as the one operating substrate. ServiceNow's CMDB says what moves, Service Mapping says with what, Cutover runs the people, Nutanix Move does the data, and a Palo Alto firewall in each cloud's hub holds the security contract. The waves are timed around the Medicare Advantage election calendar, the X12 EDI flows move as their own groups, and the evidence is kept for the HIPAA Security Rule. Seven diagrams, every claim from public documentation, including the parts of the ask the documentation doesn't support as stated.
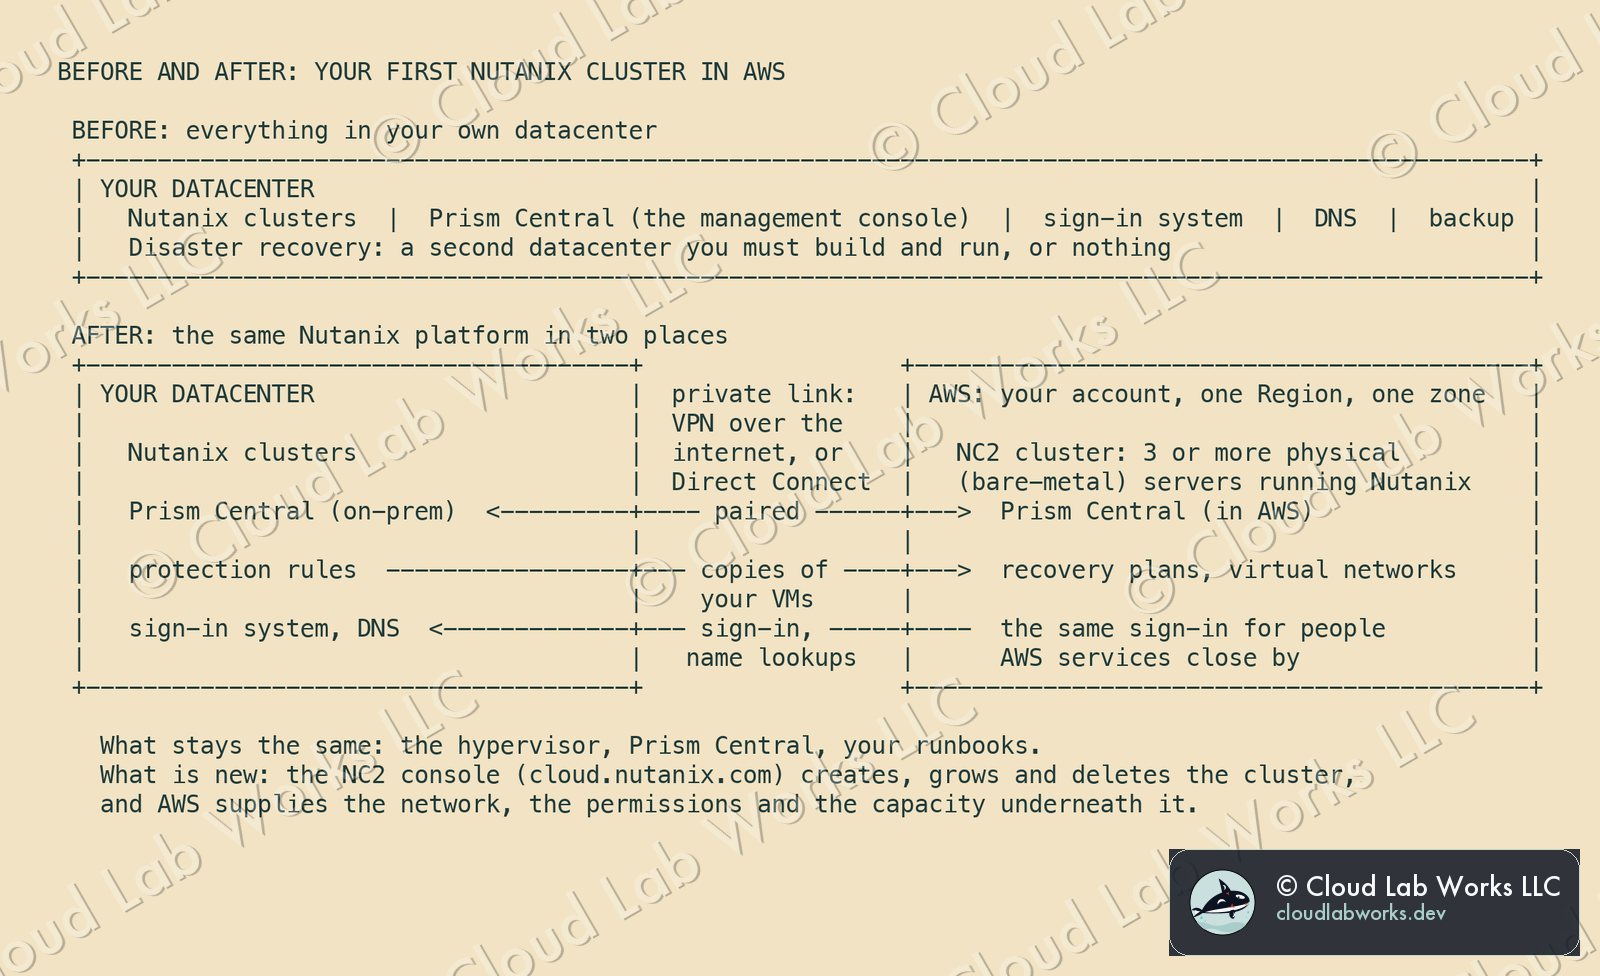
Your first Nutanix cluster in AWS, without writing a line of code
You run Nutanix in your own datacenter, you've never written infrastructure as code, and you've been asked to get a first footprint into AWS. This is the whole path for NC2 on AWS done in web consoles only: who needs to be in the room, the decisions to make first, eight steps with the clicks, what you should see when each one worked, the mistake people make at each one, and a time budget. Every term is explained the first time it appears, and there's a glossary at the end.
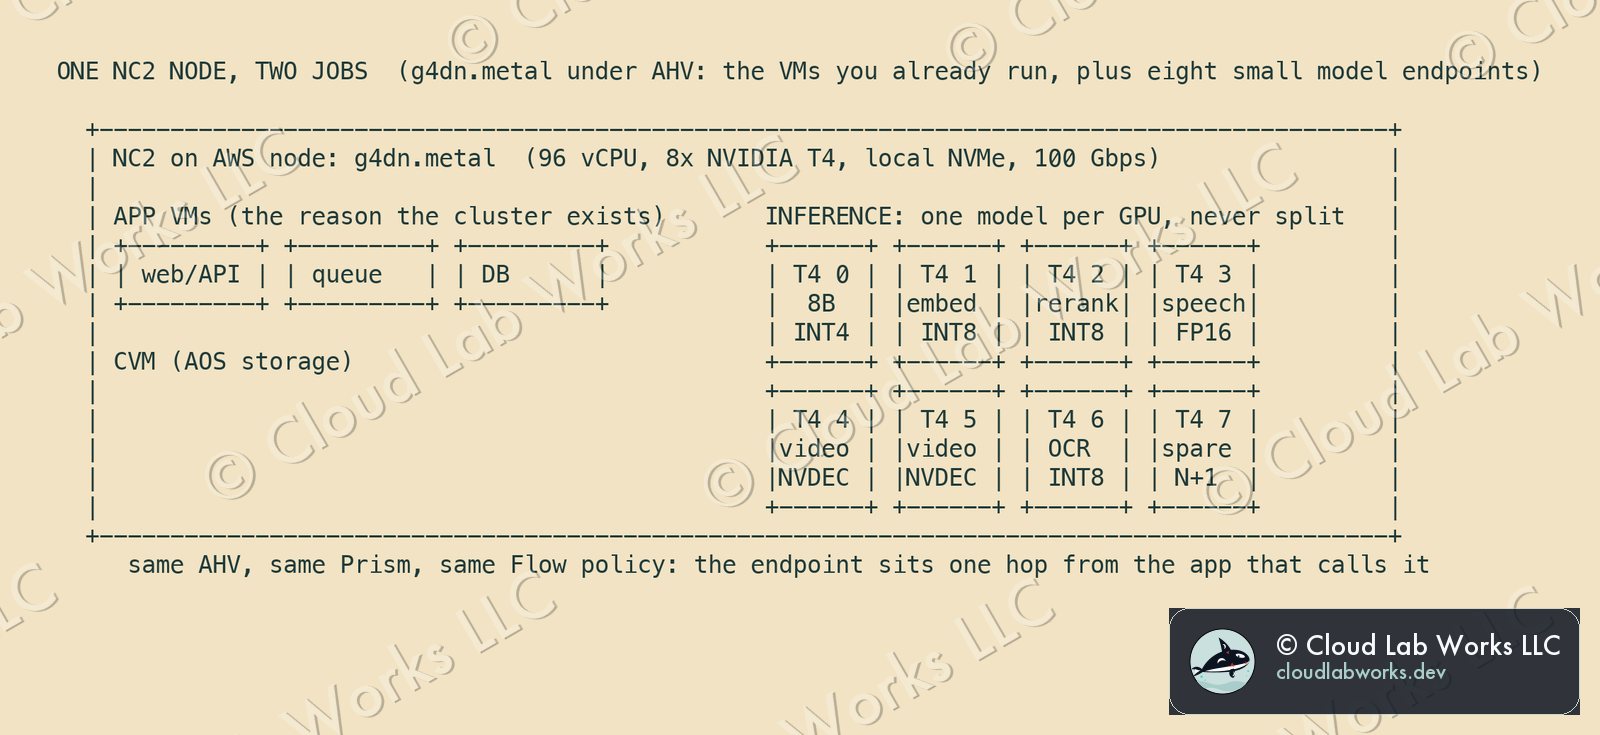
The cheap seat: edge-class inference on NC2 on AWS with the NVIDIA T4
Last week's decision record said no to the T4 for a regulated chat assistant. This is the workload where the same GPU is the right answer: many small models, one per card, beside the application VMs on the NC2 nodes you already run. Design rules, what fits in 16 GB, and what it costs the architecture.
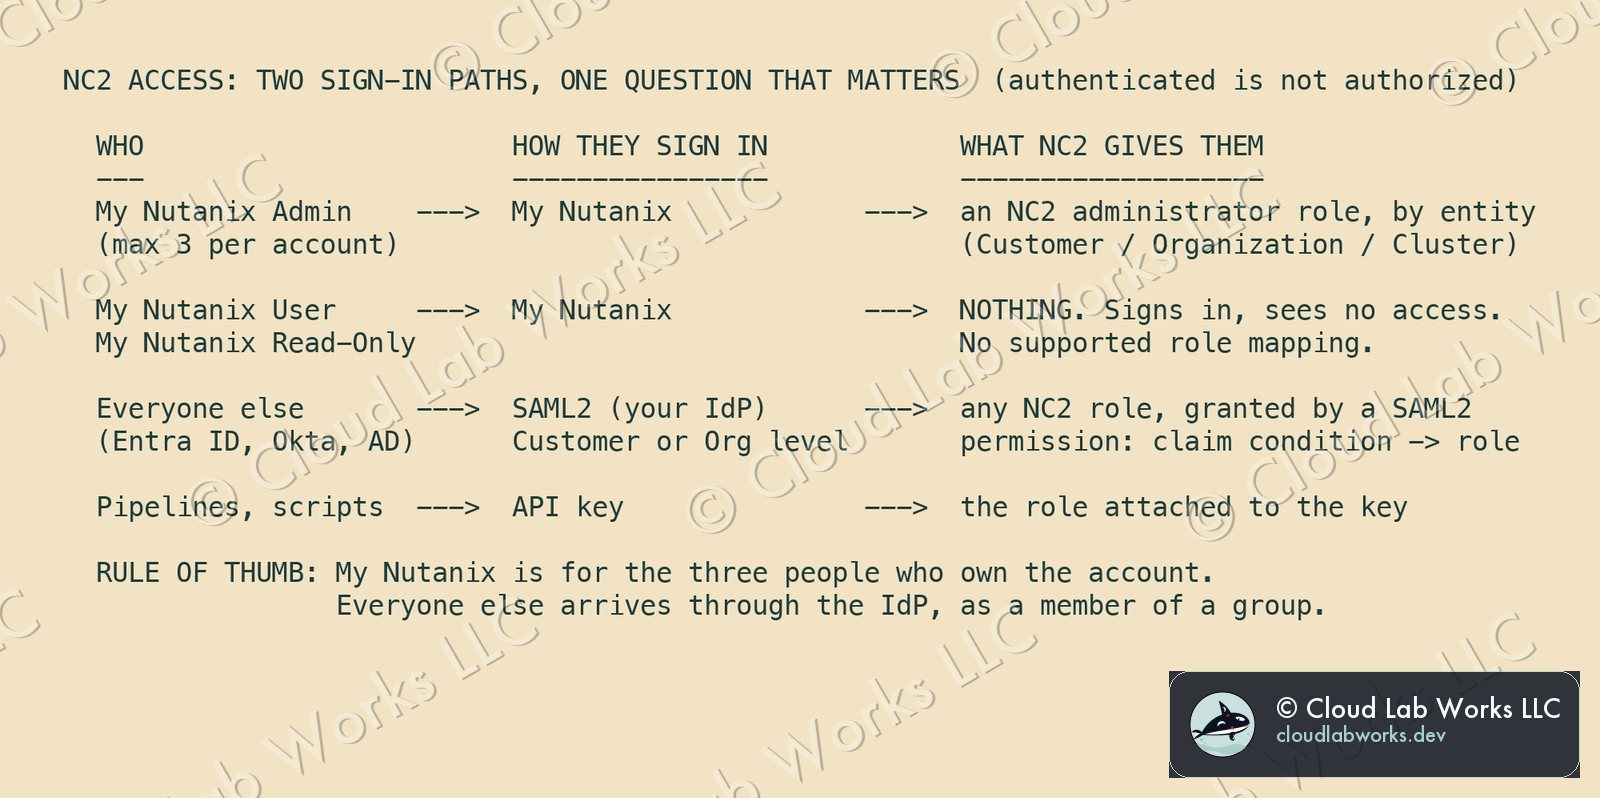
Onboarding people into NC2 without tickets: access and role mapping, done once
A common NC2 access problem isn't a bug: a user signs in with My Nutanix and sees nothing, because signing in and being allowed in are different steps. The NC2 guides spell out how the two sign-in paths map to NC2 roles. This post turns that into an onboarding design: three My Nutanix administrators, everyone else through your identity provider as a member of a group, and a role that follows the group.
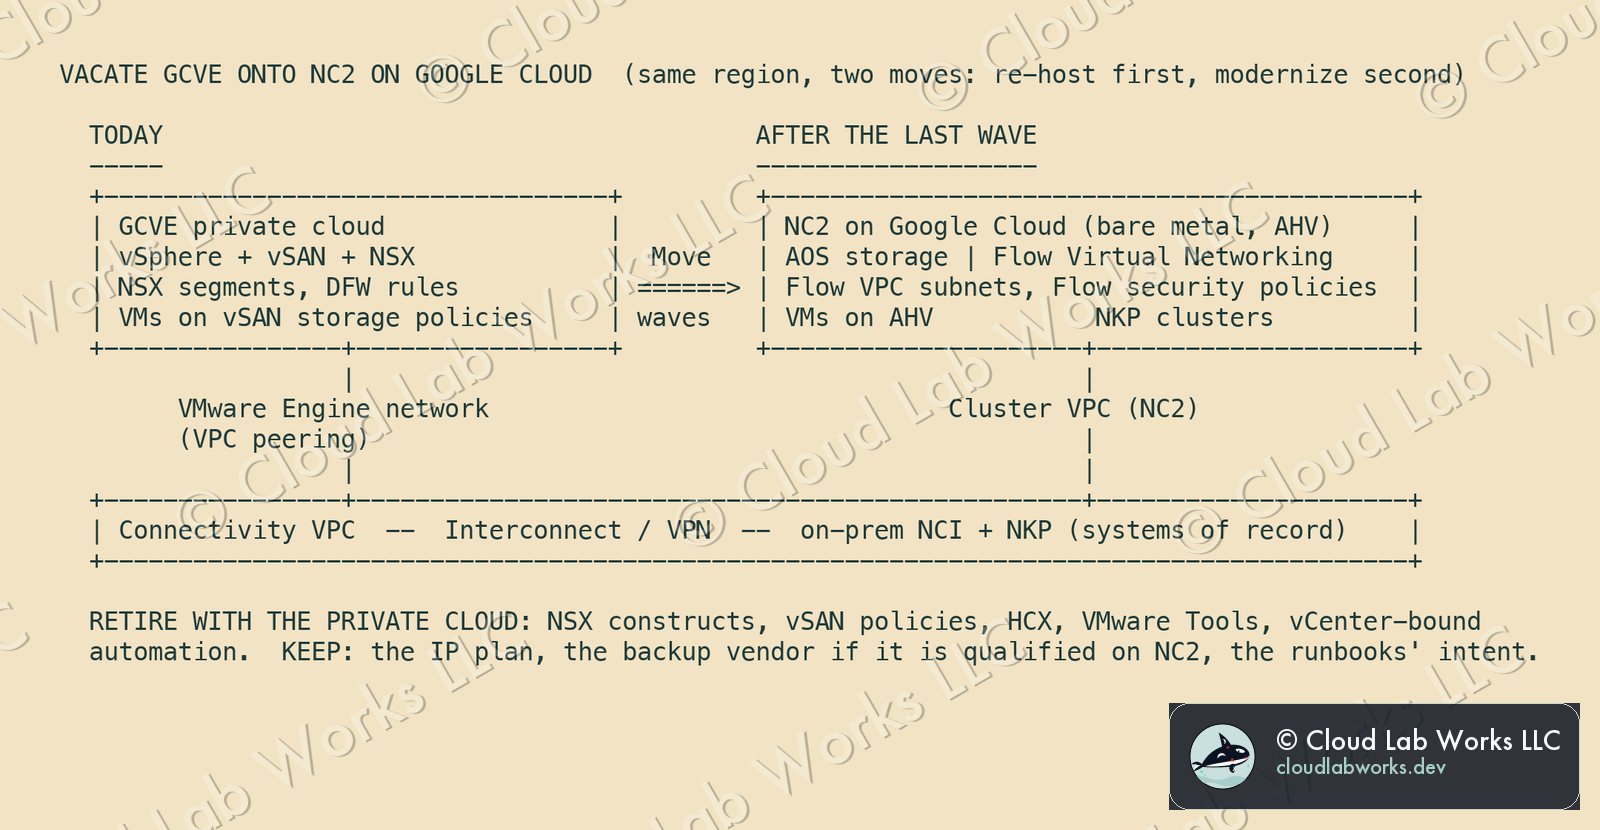
Leaving GCVE for NC2 on Google Cloud, with NKP as the destination
A customer running Google Cloud VMware Engine wants off the VMware stack without leaving Google Cloud, and wants its in-house applications on Kubernetes across Google Cloud and its own data centre. This is the route as steps: re-host onto NC2 on Google Cloud in the same region first, modernize onto NKP second, and what each step costs the architecture.
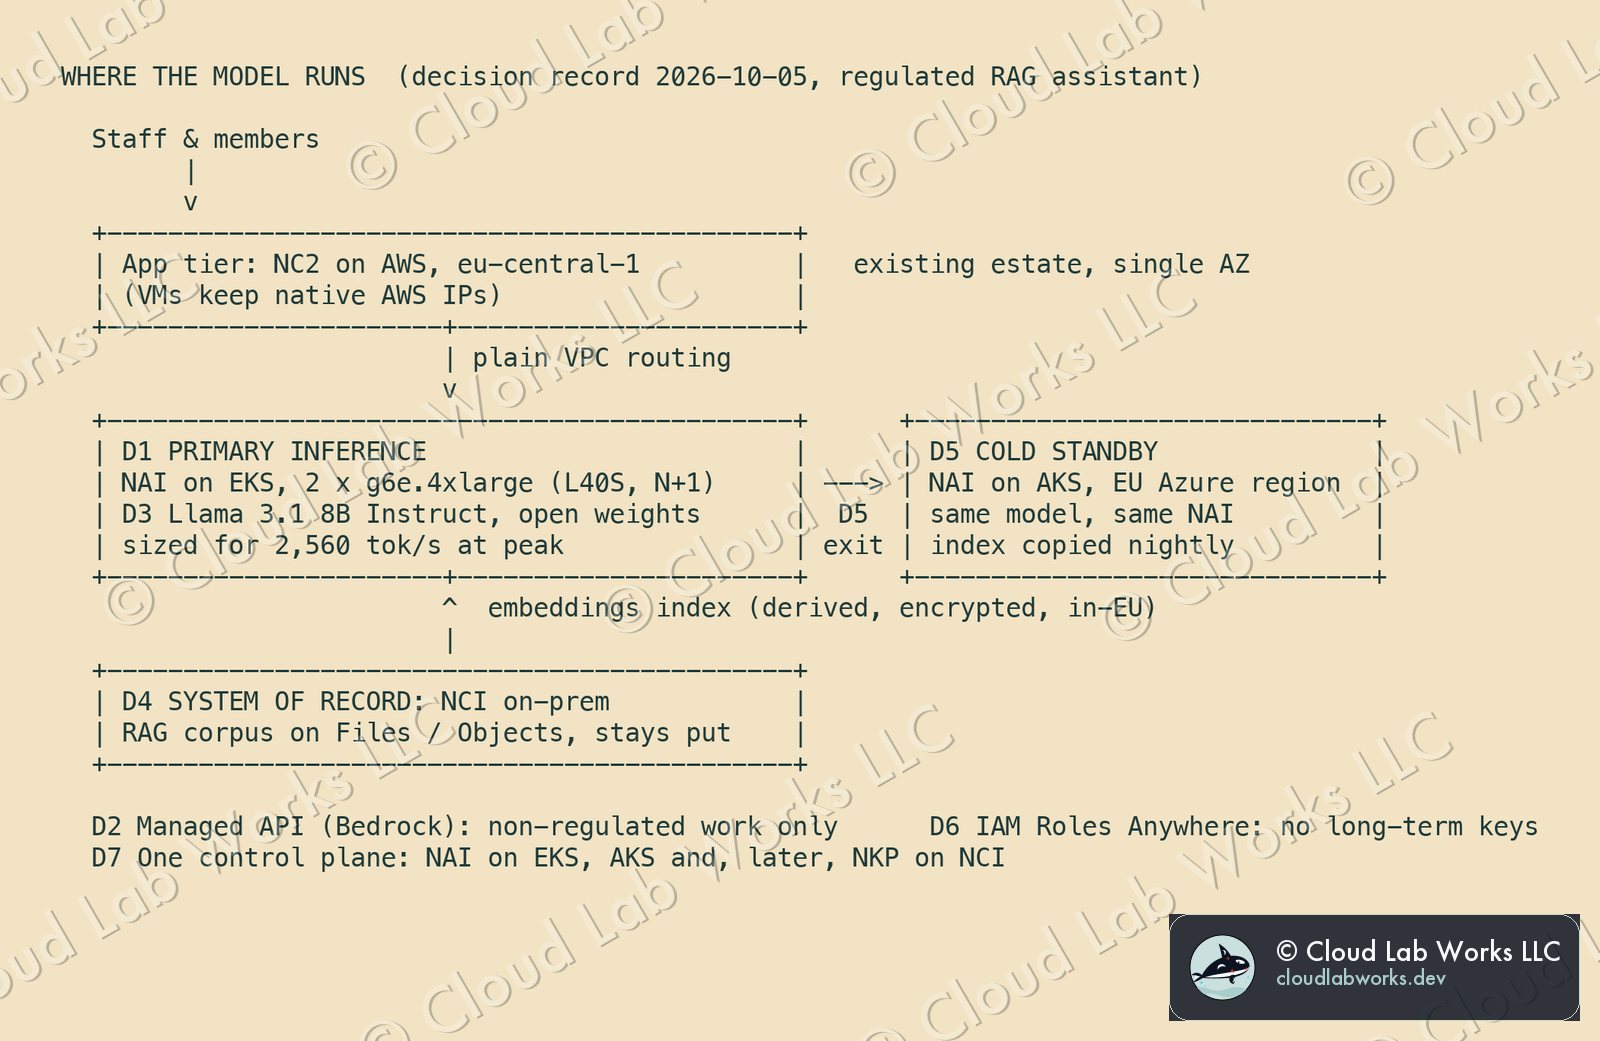
Where should the model run? A placement decision for a regulated RAG assistant across NCI, NC2 and the hyperscalers
An insurer regulated in the EU and the UK wants a private RAG assistant for its staff. The model could run on its own Nutanix clusters, next to its NC2 estate on AWS, or behind a hyperscaler's managed API. This is the decision record: seven decisions, what each one rejected, the number behind it, and what would change the answer. The short version: the managed API is about five times cheaper per token, and that is still not the deciding number.
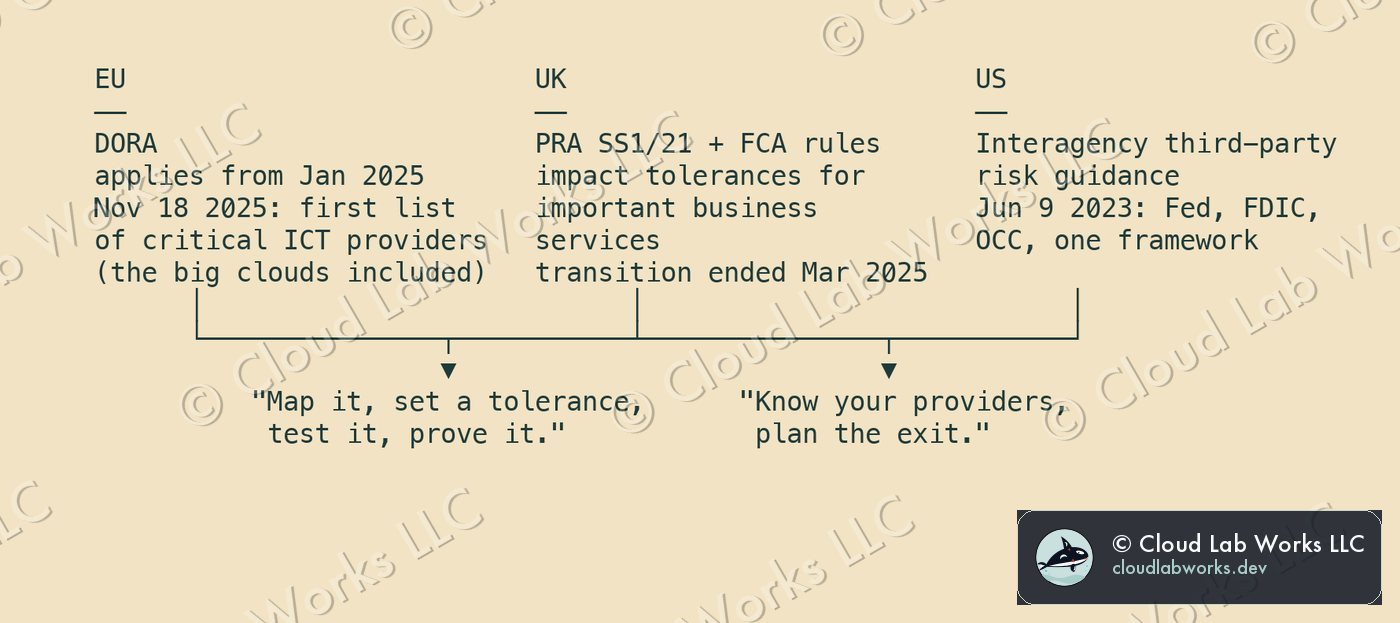
Resilience is now a regulated number: what DORA, the PRA and US third-party guidance mean for hybrid multicloud
Three regulators on two continents now ask financial institutions the same question: show us you can lose a provider and keep serving customers. DORA, the PRA's impact tolerances and the US interagency third-party guidance turn resilience from a slide into a number you have to test and defend. Here is what the three have in common, what it does to cloud architecture, and the three questions I would put to any CIO before the next exam.
The Missing Credential: How IAM Roles Anywhere Unlocks AWS AI on Nutanix Cloud Clusters
Every hybrid AI conversation hits the same wall, and it is never bandwidth or the model. It is a credential. An AHV guest on NC2 is not an EC2 instance, so it has no instance profile and the SDK finds nothing. AWS IAM Roles Anywhere closes that gap with X.509 certificates and temporary credentials, which lets a fraud scoring VM call SageMaker and Bedrock over PrivateLink without refactoring, rehosting, or moving the regulated data off the cluster. Production shape is multi-AZ and multi-region on i7i metal. ASCII and Mermaid at every step.
NC2 across AWS, Azure and Google Cloud: active/active/standby on the v4 API, with a native service beside each cluster
The real point: a Nutanix UVM on NC2 sits in a plain VPC or VNet, so talking to a native cloud service next to it takes no Nutanix-specific plumbing at all — the v4 API sets up standard networking and gets out of the way. Proven with an active/active/standby pattern across AWS, Azure and Google Cloud (Prism Central's v4 dataprotection API for the failover, a data lake, a Function and a Looker instance for the native-service half) — and a straight look at where the two earlier build posts still lean on the console and the v2 API, and what full v4 buys back. ASCII at every step. Design pattern from the published v4 specs; not run end-to-end against three live clusters.
NC2 on Azure, as code: Bicep for the landing zone, the NC2 v2 API for the organization, the cloud account and the cluster
The Azure twin of yesterday's AWS walkthrough, with one difference that matters: on Azure the NC2 console never has to be clicked. Bicep builds the tenant side (custom role, app registration, the three VNets with their delegated subnets, NAT gateways, peering, Route Server), and the NC2 v2 API creates the organization, the cloud account and the cluster with Prism Central and Flow Gateways inside it. ASCII at every step; OpenTofu on the v4 APIs takes over where yesterday's post did.
NC2 on AWS, as code: the NC2 console to the first VM with the v4 APIs and OpenTofu
Nutanix Cloud Clusters on AWS has no Prism Element to log into: with Flow Virtual Networking you are Prism Central–bound from the first minute. One walkthrough, ASCII at every step: onboarding the AWS account in the NC2 console, the URLs and ports to allowlist, the cluster and Prism Central in one create, then OpenTofu on the v4 APIs for VPCs, subnets, floating IPs and the first VM.