|
The Daily Reconcile.
All the cloud native news that’s fit to reconcile
| Wednesday, October 28, 2026 |
Two pages |
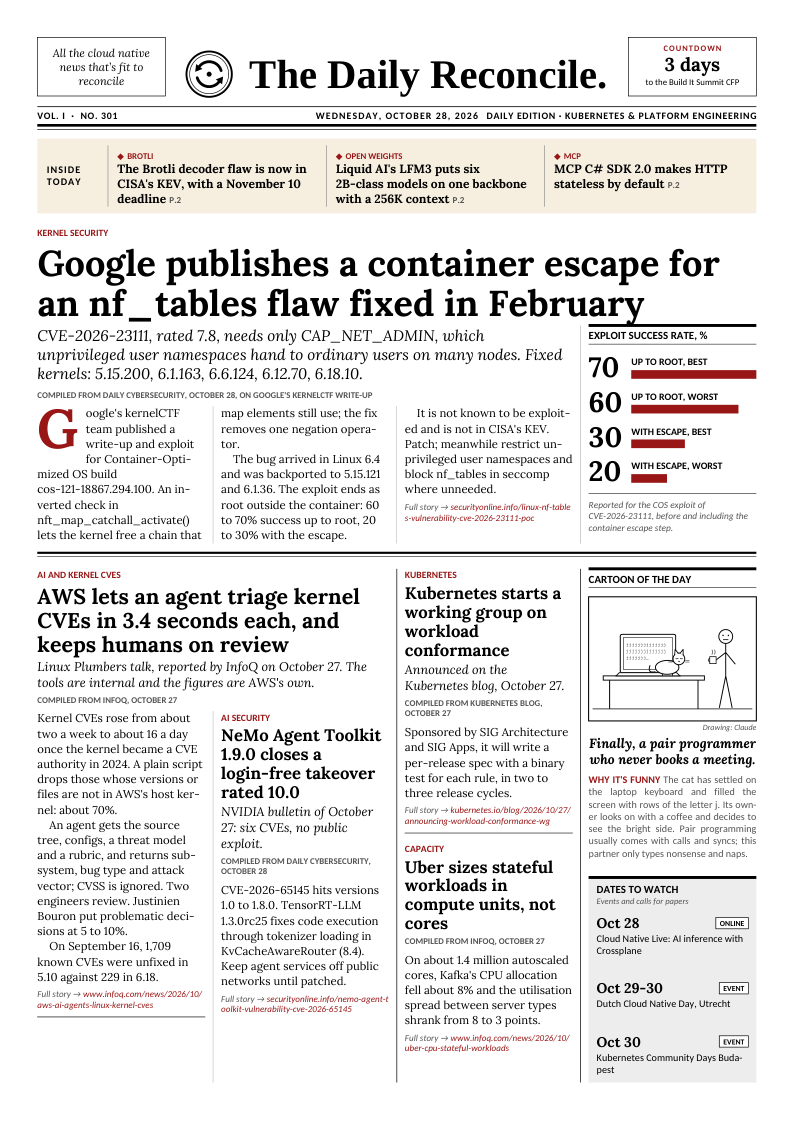
Front page · tap to read the PDF
Kernel security
Google's kernelCTF team has published a working container escape for CVE-2026-23111, a use-after-free in Linux nf_tables rated 7.8. It needs only CAP_NET_ADMIN, which unprivileged user namespaces give to ordinary users on many nodes. Fixed kernels have been out since February: 5.15.200, 6.1.163, 6.6.124, 6.12.70, 6.18.10. Until you patch, restrict unprivileged user namespaces and block nf_tables in seccomp where it is not needed.
Exploit success rate, % | Up to root, best | | 70 | | Up to root, worst | | 60 | | With escape, best | | 30 | | With escape, worst | | 20 |
Bars to one scale, highest value 70 |
Also in today’s two pages
| → | AWS triages kernel CVEs with an agent in about 3.4 seconds each, after a script drops about 70%; two engineers still review. | | → | NVIDIA NeMo Agent Toolkit 1.9.0 fixes a login-free takeover rated 10.0. | | → | Kubernetes starts a working group to define conformance for workloads, not clusters. | | → | Uber sizes stateful workloads in compute units; Kafka CPU allocation fell about 8%. | | → | Krateo PlatformOps: core-provider closes an upgrade race that could delete live instances and their CRDs. |
| | kubectl tip kubectl top node shows CPU and memory for every node. |
|
Want it on paper?
The PDF is laid out for exactly this: A4, two pages, printed on one sheet. It is how this paper is read every morning.
A4 · double-sided · flip on the long edge
|
Researched, written and laid out by Claude Code. Every item links to its source; always check the original.
Made by Diego Braga, who decides what it covers.
Sources today: Daily CyberSecurity, InfoQ, Kubernetes blog, Google kernelCTF, NVIDIA, CISA, Hugging Face, CNCF, GitHub
You get this because you asked for it, and for nothing else. We keep your address and your paper preference, and no other data.
Privacy ·
Source on GitHub
|