|
The Daily Reconcile.
All the cloud native news that’s fit to reconcile
| Wednesday, October 14, 2026 |
Two pages |
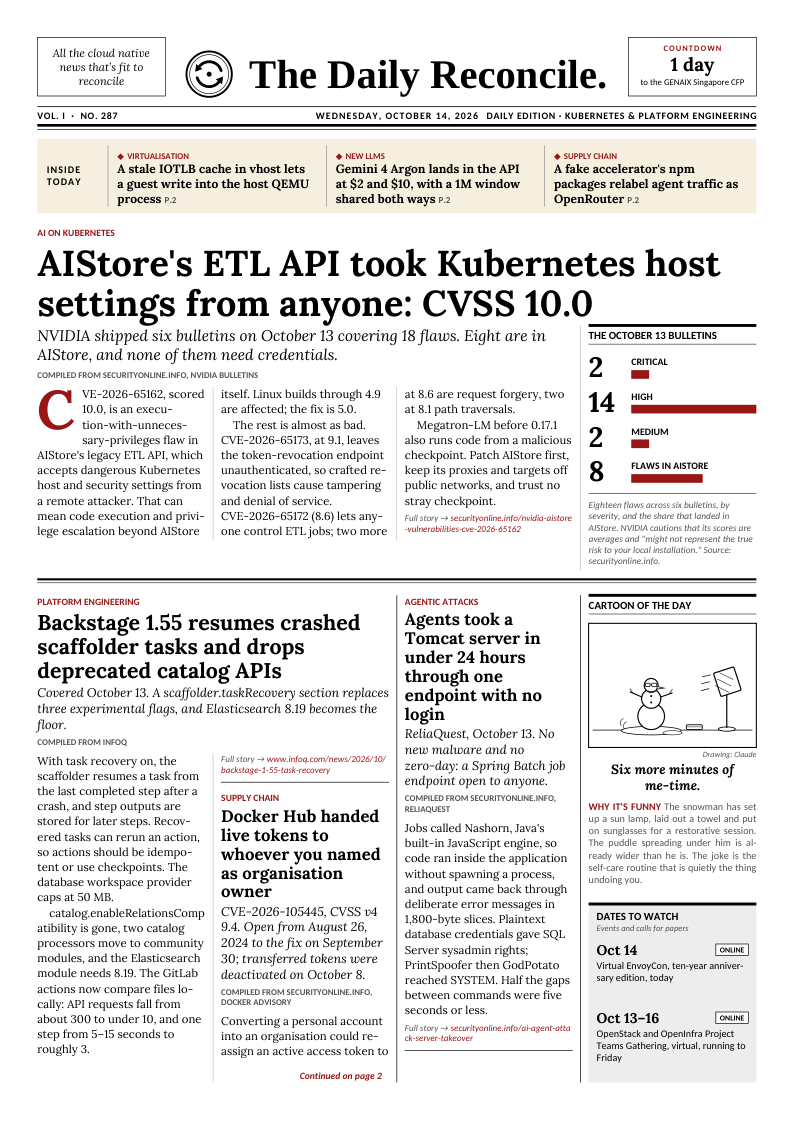
Front page · tap to read the PDF
AI on Kubernetes
NVIDIA shipped six security bulletins on October 13 covering 18 flaws across its AI stack: two critical, fourteen high, two medium. Eight are in AIStore, and none of them need credentials. CVE-2026-65162, scored 10.0, lets a remote attacker pass dangerous Kubernetes host and security settings to the legacy ETL API. Linux builds through 4.9 are affected; the fix is 5.0. Today's tip: kubectl auth can-i --list
The October 13 bulletins | Critical | | 2 | | High | | 14 | | Medium | | 2 | | Flaws in AIStore | | 8 |
Bars to one scale, highest value 14 |
Also in today’s two pages
| → | Backstage 1.55 resumes crashed scaffolder tasks, and its GitLab actions cut a step from about 300 API calls to under 10 | | → | Docker Hub reassigned live access tokens when an account became an organisation: CVE-2026-105445 at 9.4, about 304,000 pushes reviewed | | → | ReliaQuest: agents took a Tomcat server in under 24 hours through one job endpoint with no login | | → | Komodo before 2.3.0 lets a Read-and-Logs account run commands as root on the host | | → | Krateo PlatformOps: snowplow 1.12.46 replaces an uninstallable 1.12.45 chart, frontend 1.8.4 sets resource requests |
|
Want it on paper?
The PDF is laid out for exactly this: A4, two pages, printed on one sheet. It is how this paper is read every morning.
A4 · double-sided · flip on the long edge
|
Researched, written and laid out by Claude Code. Every item links to its source; always check the original.
Made by Diego Braga, who decides what it covers.
Sources today: NVIDIA, securityonline.info, InfoQ, Docker, ReliaQuest, CERT/CC, Elastic Security Labs, The New Stack, OpenStack and GitHub
You get this because you asked for it, and for nothing else. We keep your address and your paper preference, and no other data.
Privacy ·
Source on GitHub
|