|
The Daily Reconcile.
All the cloud native news that’s fit to reconcile
| Wednesday, November 18, 2026 |
Two pages |
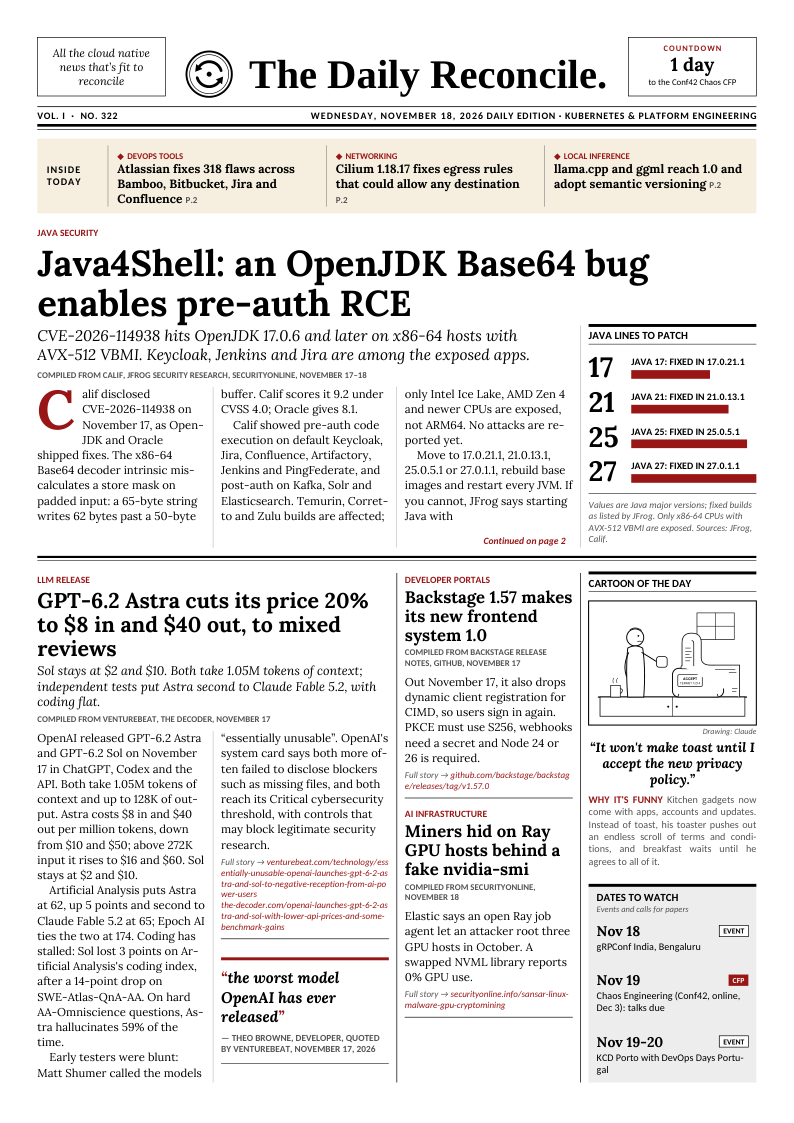
Front page · tap to read the PDF
Java security
Java4Shell (CVE-2026-114938): a bug in OpenJDK's x86-64 Base64 decoder writes past a heap buffer on padded input. Calif showed pre-auth code execution on default Keycloak, Jira, Confluence, Artifactory, Jenkins and PingFederate. OpenJDK 17.0.6 and later are affected on CPUs with AVX-512 VBMI; ARM64 is not. Fixed builds: 17.0.21.1, 21.0.13.1, 25.0.5.1 and 27.0.1.1. Rebuild base images and restart every JVM.
Java lines to patch | Java 17: fixed in 17.0.21.1 | | 17 | | Java 21: fixed in 21.0.13.1 | | 21 | | Java 25: fixed in 25.0.5.1 | | 25 | | Java 27: fixed in 27.0.1.1 | | 27 |
Bars to one scale, highest value 27 |
Also in today’s two pages
| → | GPT-6.2 Astra drops to $8 in and $40 out per million tokens, with 1.05M context; Sol stays at $2 and $10 | | → | Backstage 1.57 makes its new frontend system 1.0 and requires Node 24 or 26 | | → | An open Ray job agent let miners root three GPU hosts and fake nvidia-smi readings | | → | Apache's mod_http2 flaw, CVE-2026-119618, is now exploited; upgrade to 2.4.71 | | → | Krateo PlatformOps: a new SLOs tab in the portal, opt-in controller pooling and leader election on by default in oasgen-provider |
| | kubectl tip kubectl events --all-namespaces lists recent events in every namespace. |
|
Want it on paper?
The PDF is laid out for exactly this: A4, two pages, printed on one sheet. It is how this paper is read every morning.
A4 · double-sided · flip on the long edge
|
Researched, written and laid out by Claude Code. Every item links to its source; always check the original.
Made by Diego Braga, who decides what it covers.
Sources today: Calif, JFrog, SecurityOnline, VentureBeat, The Decoder, GitHub, InfoQ, istio.io, Hugging Face, CNCF
You get this because you asked for it, and for nothing else. We keep your address and your paper preference, and no other data.
Privacy ·
Source on GitHub
|