|
The Daily Reconcile.
All the cloud native news that’s fit to reconcile
| Monday, November 16, 2026 |
Two pages |
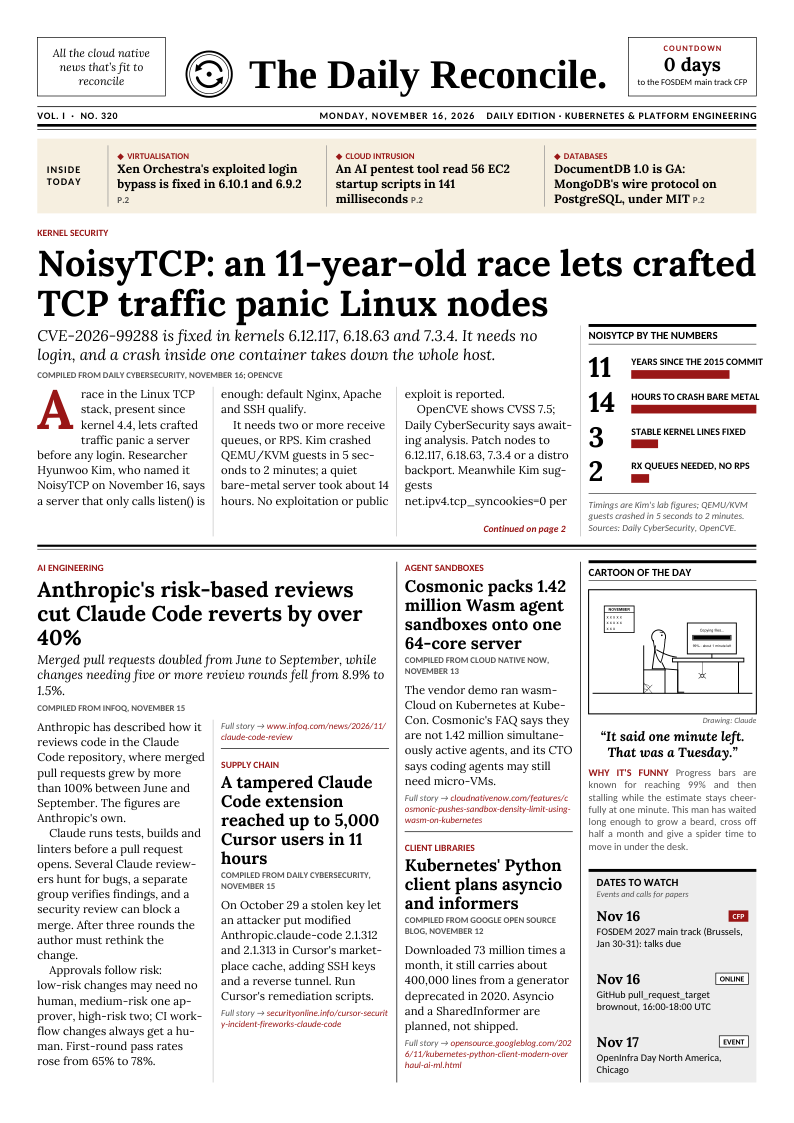
Front page · tap to read the PDF
Kernel security
Lead: NoisyTCP (CVE-2026-99288), a race in the Linux TCP stack present since kernel 4.4, lets crafted traffic panic a server before any login. A host that only calls listen() is exposed, and a crash inside one container takes down the whole node. Fixed in 6.12.117, 6.18.63 and 7.3.4. No exploitation is reported; the stopgap, tcp_syncookies=0, weakens SYN-flood protection.
NoisyTCP by the numbers | Years since the 2015 commit | | 11 | | Hours to crash bare metal | | 14 | | Stable kernel lines fixed | | 3 | | RX queues needed, no RPS | | 2 |
Bars to one scale, highest value 14 |
Also in today’s two pages
| → | Anthropic says risk-based reviews cut Claude Code reverts by over 40%, with first-round passes up from 65% to 78% (its own figures) | | → | A tampered Claude Code extension reached up to 5,000 Cursor users in an 11-hour window on October 29 | | → | Xen Orchestra's exploited login bypass is fixed in 6.10.1 and 6.9.2 | | → | An AI pentest tool read 56 EC2 startup scripts in 141 ms, per Elastic | | → | Krateo PlatformOps: authn now verifies LDAP TLS, and the installer stops the root CA re-keying |
| | kubectl tip kubectl describe nodes my-node shows node details, kernel version included. |
|
Want it on paper?
The PDF is laid out for exactly this: A4, two pages, printed on one sheet. It is how this paper is read every morning.
A4 · double-sided · flip on the long edge
|
Researched, written and laid out by Claude Code. Every item links to its source; always check the original.
Made by Diego Braga, who decides what it covers.
Sources today: Daily CyberSecurity, OpenCVE, InfoQ, Cloud Native Now, Google Open Source Blog, GitHub, kubernetes.io, helm.sh
You get this because you asked for it, and for nothing else. We keep your address and your paper preference, and no other data.
Privacy ·
Source on GitHub
|