sanitised. IoT & ICS/OT Daily Briefing · Sunday 25 October 2026
Today in IoT & ICS/OT
 |
IoT & Hardware
BlackX UEFI bootkit exploits Baton Drop flaw to bypass Secure Boot
BleepingComputer
A new UEFI bootkit named BlackX, deployed in an espionage campaign in early 2026, exploited the old Baton Drop vulnerability to bypass Secure Boot and load a malicious driver designed to interfere with security solutions from Kaspersky and Avast. [...]
|
|
Catch up
Recent IoT & ICS/OT stories you haven't had in a briefing yet.
|
|
 |
IoT & Hardware
Hackers Use New BlackX Bootkit to Bypass Windows Secure Boot on Fully Patched Systems
Cyber Security News · 23 Oct
A new UEFI bootkit called BlackX has been used in cyberespionage attacks against diplomatic organizations in Tajikistan, Uzbekistan, and Turkmenistan. The malware targets Secure Boot, a feature designed to help stop untrusted software from running before Windows starts. Researchers say the infected computers had receiv…
|
|
 |
ICS / OT & Critical Infrastructure
UK threatens subsea cable saboteurs with 14 years behind bars
The Register (Security) · 23 Oct
Whitehall wants tougher penalties and new powers over telecoms operators as Russian activity raises alarm Britain is threatening subsea cable saboteurs with up to 14 years in prison and unlimited fines, having apparently decided that Victorian-era laws aren't quite up to the job of keeping Russian submarines away from …
|
|
 |
IoT & Hardware
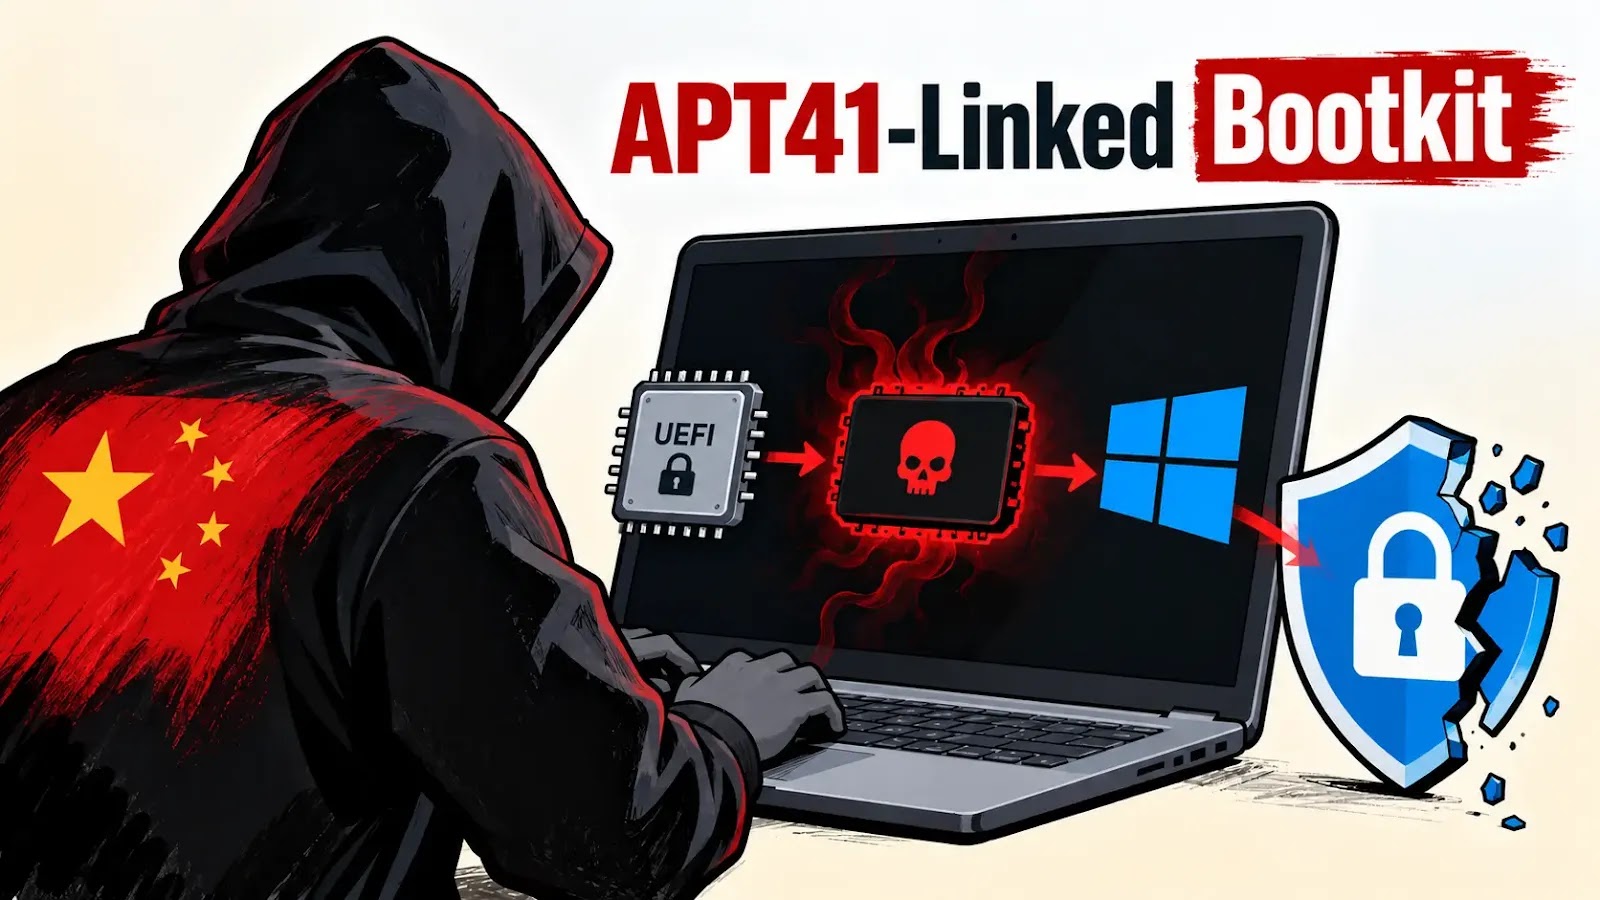
Suspected Chinese APT41 Hackers Use BlackX Bootkit to Bypass Windows Secure Boot
GBHackers · 23 Oct
Suspected Chinese APT41 hackers have deployed BlackX, a UEFI bootkit, against diplomatic organizations in Tajikistan, Uzbekistan, and Turkmenistan. Researchers attribute the operation to APT41 with medium confidence. BlackX closely resembles BlackLotus, the bootkit advertised on underground forums for $5,000 in October…
|
|
Also in security today
 |
Vulnerabilities & Exploits
Will AI expose the rickety infrastructure of the internet?
TechCrunch (Security)
Buy One Founder Summit Ticket, Get a Second for Free. Register now. Disrupt doors open Oct. 13. Get your pass and bring someone with you at 50% off. REGISTER NOW. A startling announcement went out earlier this week: Due to recently discovered vulnerabilities in the open source programming language PHP, website owners h…
|
|
 |
Vulnerabilities & Exploits
Pierluigi Paganini answers questions about the PHP2Shell flaws
Security Affairs
Pierluigi Paganini answers questions about the PHP2Shell vulnerability, early exploitation, AI-assisted attacks, and the risks to businesses, servers, and personal data. 1. Your latest report reveals that hackers began exploiting the PHP2Shell vulnerability four days before it was publicly disclosed. First, can you exp…
|
|
 |
Vulnerabilities & Exploits
U.S. CISA adds Collabora Online flaw to its Known Exploited Vulnerabilities catalog
Security Affairs
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Collabora Online flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a Collabora Collabora Online – Built-in CODE Server flaw, tracked as CVE-2026-110447 (CVSS score of 9.2), to its …
CVE-2026-110447
|
|
