November 8, 2022
Between Two Nerds is a weekly discussion between Tom a Uren and myself. We cover interesting topics, and this week’s show is no exception. Feast your occipital lobes on this:
Between Two Nerds: Why does Europe suck? - Risky Business Media
-
Administrivia: I’m still figuring out how to incorporate Mastodon content. Right now I copy the content and include a link to the post. Im not sure I like it. I’ll keep trying. Why not subscribe and join me on this journey?
-
-
Awesome Malware Techniques - A curated list of resources to analyse and study malware techniques:
GitHub - fr0gger/Awesome_Malware_Techniques: This is a repository of resource about Malware techniques · GitHub
This is a repository of resource about Malware techniques - fr0gger/Awesome_Malware_Techniques
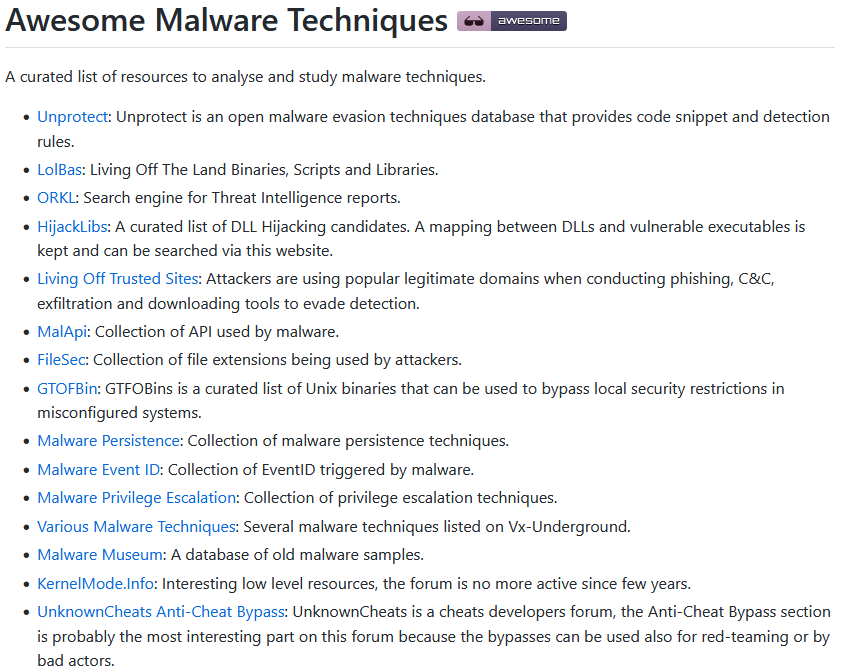
Philippe Lagadec: "Awesome Malware Techniques - A curated list of re…" - Mastodon.social
Attached: 1 image Awesome Malware Techniques - A curated list of resources to analyse and study malware techniques: https://github.com/fr0gger/Awesome_Malware_Techniques by @fr0gger
-
A new CrackMapExec module just landed courtesy of our Aurélien Chalot.
It makes use of token impersonation to execute commands as different logged in users (ala meterpreter's incognito module originally from Luke Jennings).
Aurélien did a full writeup of his work, as well as released a stand alone tool.
Standalone tool: https://github.com/sensepost/impersonate
CME commit: https://github.com/Porchetta-Industries/CrackMapExec/pull/601

SensePost: "A new CrackMapExec module just landed courtesy of…" - Infosec Exchange
Attached: 1 image A new CrackMapExec module just landed courtesy of our Aurélien Chalot. It makes use of token impersonation to execute commands as different logged in users (ala meterpreter's incognito module originally from Luke Jennings). Aurélien did a full writeup of his work, as well as released a stand alone tool. Writeup: https://sensepost.com/blog/2022/abusing-windows-tokens-to-compromise-active-directory-without-touching-lsass/ Standalone tool: https://github.com/sensepost/imperso...
-
Russian Aerospace Forces conducted significantly more extensive fixed-wing strike operations during the first days of the invasion than has been previously documented, while Ukrainian air-defence capabilities were suppressed by initial attacks
Nov 7, 2022
The Russian Air War and Ukrainian Requirements for Air Defence
Further Western support is needed to ensure that Kyiv can counter Moscow’s updated approach to the air war in Ukraine.

-
**U.S. Attorney Announces Historic $3.36 Billion Cryptocurrency Seizure And Conviction In Connection With Silk Road Dark Web Fraud**
https://www.justice.gov/usao-sdny/pr/us-attorney-announces-historic-336-billion-cryptocurrency-seizure-and-conviction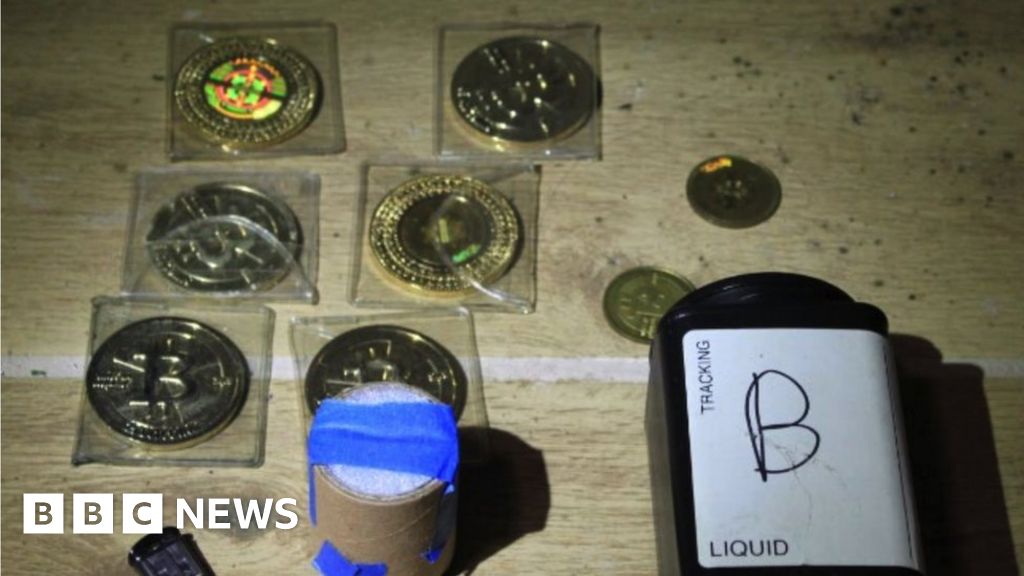
Stolen $3bn Bitcoin mystery ends with popcorn tin discovery
James Zhong pleads guilty to the 2012 hack as police find stash of 50,000 Bitcoin.
-
Artificial intelligence (AI) and machine learning (ML) are increasingly being used in every aspect of our life. We have developed comprehensive principles to help protect AI and ML systems against exploitation.
Nov 7, 2022
Introducing our new machine learning security principles
Why the security of artificial intelligence (AI) and machine learning (ML) is important, how it’s different to standard cyber security, and why the NCSC has developed specific security principles.

-
More details on an older GRU Illegal exposure.
Breaking: Norwegian authorities named the real identity of the fake "Brazilian researcher": his name is Mikhail Mikhushin, born 1978. This announcement is in line with what we, together with our investigative partners, had already discovered, and I will add some more details:
Oct 28, 2022

-
Crypto. Scam. Fraud. Lol
The NFTs minted on OpenSea in its "shared storefront" have a backdoor. OpenSea can transfer any of them just like the "owner" of the tokens. See below for exploit script, and how to see if your tokens are affected.
Nov 7, 2022

-
Automatic signatures work quite well now in @rizinorg ! Just run `rizin -A binary` and it will match functions in your binary with sigdb, a library Rizin come with. You can also generate/apply FLIRT signatures with the `F` commands in Rizin shell. Thanks to @Der0ad for the work!
Nov 7, 2022

-
Two years ago, I published #TinyCheck. An application to passively detect signs of compromise by examining network flows. Today, I'm releasing a forked and enhanced version of it, dubbed #SpyGuard. Some evolutions in this thread 🚀(1/7) github.com/SpyGuard
Nov 7, 2022
SpyGuard - Overview
SpyGuard has one repository available. Follow their code on GitHub.

-
an insecure narcissist buying a criticism factory
Nov 7, 2022

-
Microsoft sued for piracy through CoPilot.
Good. Training an AI on loads of content created by people without compensating them or honouring their licenses is wrong, whether art or code or text or whatever.
https://www.bleepingcomputer.com/news/security/microsoft-sued-for-open-source-piracy-through-github-copilot/-
I'm happy to announce the completion of my (somewhat contrarian) guide to photography for geeks: 📷 lcamtuf.coredump.cx/photo_basics/ Whether you carry a smartphone or a $5,000 rig, my hope is to help you discover the joy of experimenting with simple (and effective) photo techniques.
Oct 15, 2022

-
Remember German car industry giant Continental stating in August that they had repelled a cyber attack? Turns out that they have lost 40TB and face a ransom demand from Lockbit ransomware group....1/2 @thegrugq
Nov 8, 2022
Continental: Hacker stehlen offenbar 40 Terabyte Daten
Die berüchtigte Cybercrime-Gruppe Lockbit hat laut einem Medienbericht den deutschen Autozulieferer Continental erpresst. Die Täter hatten demnach zuvor große Mengen an Unternehmensdaten entwendet.

-
As security researchers, we don’t often discuss failed research projects. While it may be a bit embarrassing to not succeed, there are still lessons learned from the project. In this thread, I’d like to share research I’ve been doing on-and-off on identifying AWS honeytokens. 🧵
Nov 7, 2022

-
"On Tuesday 8 November, Sophie In ‘t Veld, the rapporteur for the Inquiry Committee investigating Pegasus and equivalent spyware, will present a first version of their results."

Press conference on draft findings of EP spyware inquiry | News | European Parliament
On Tuesday 8 November, Sophie In ‘t Veld, the rapporteur for the Inquiry Committee investigating Pegasus and equivalent spyware, will present a first version of their results.
Press conference recording here: https://multimedia.europarl.europa.eu/en/webstreaming/press-conference-by-sophie-in-t-veld-rapporteur-on-pega-draft-report_20221108-1100-SPECIAL-PRESSER
https://mastodon.social/@campuscodi/109308101589718654-

Add a comment: