March 1, 2023
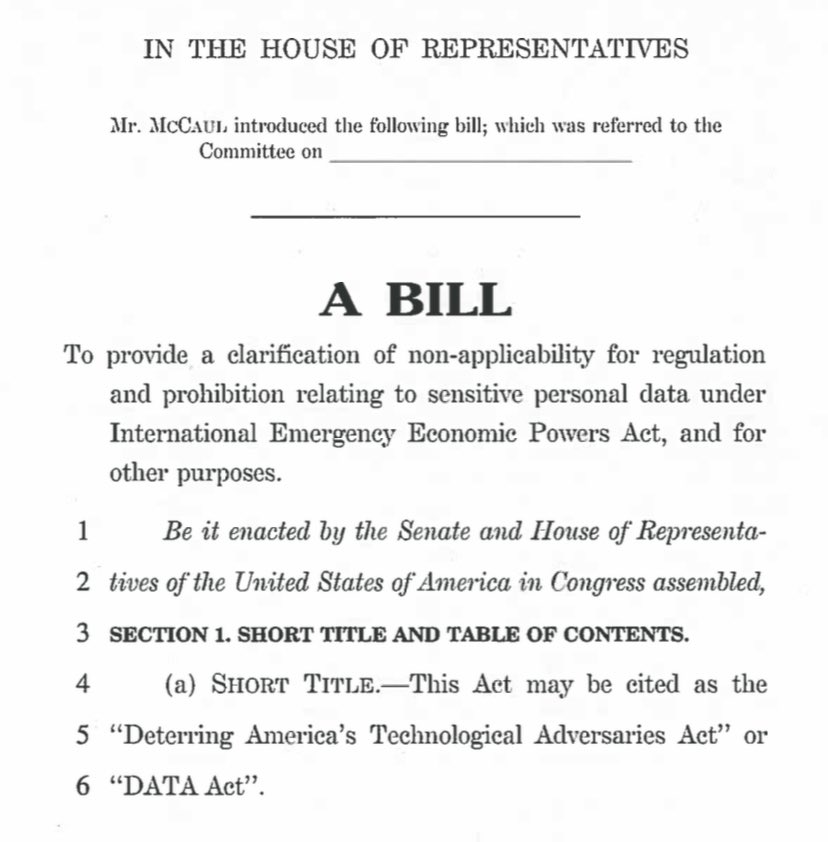
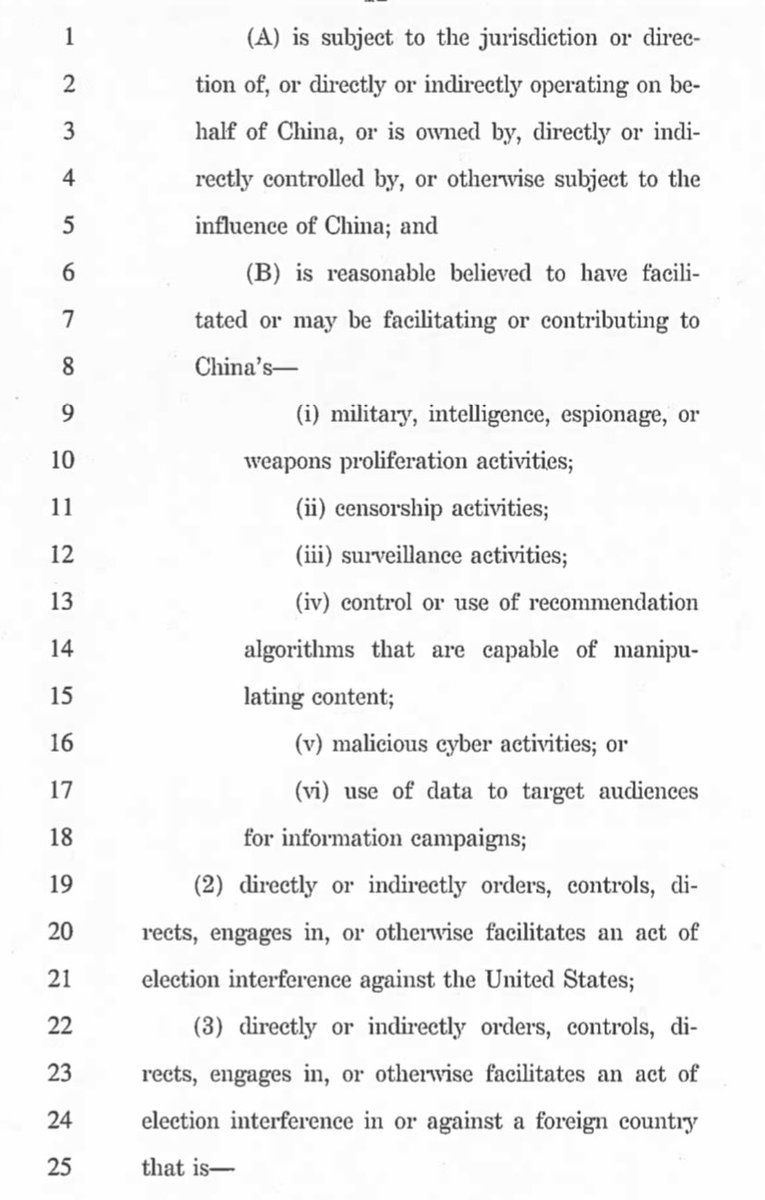
U.S. Congress to vote on a law that would make it easy to prohibit foreign apps. Like TikTok, explicitly mentioned in the proposal. A complete. Ban. Considered. This all-thing is going very fast. congress.gov/bill/118th-con… docs.house.gov/meetings/FA/FA…
Feb 28, 2023

-
Many thanks for this wonderful collaboration, @DrSNewbery !! @IICRR @HumanitiesDCU @DCU @USWPolResearch @USWPolicing_Sec @USWISRM @eucter @euacademy_dcu @ErasmusIMSISS
Feb 22, 2023
Critical Intelligence Studies: A new framework for analysis
As the purpose of the study of intelligence is, in part, to aid the practice of intelligence, scholarship must reflect that practice. This article sets out a theoretical framework for Critical Inte...

-
A collection of jailbreak prompts for ChatGPT
-
Re: LastPass: I will repeat, I simply don't trust cloud storage of password safes. It's too tempting a target.
Mar 1, 2023

-
Війна вносить трагічні елементи в персональну модель кіберзагроз. Випадки, коли наші воїни гинуть, а їхні гаджети стають здобиччю ворога, зараз трапляються чи не щодня. Як наслідок, ворог часто отримує цінний цифровий актив – кіберперсону загиблого воїна. 2/9
Feb 28, 2023

War introduces tragic elements into the personal model of cyber threats. Cases when our soldiers die, and their gadgets become the prey of the enemy, now happen almost every day. As a result, the enemy often receives a valuable digital asset – the cyber persona of the fallen soldier. 2/9
By unlocking the device with a fingerprint or face, enemy intelligence can use the stolen identity of a service member. 3/9
You can combat such methods by turning off biometrics to unlock the device. Unlock the device by pin code, and turn on biometrics to unlock sensitive applications inside the gadget. 4/9
-
Hot-take: I don't think "vendor consolidation" is a priority for serious infosec ppl. "none of this works" is more common than "all this works but i hate having multiple vendors" Aside from Microsoft, i can't think of many reasonable "just buy it from the consolidator" options
Mar 1, 2023

-
Random exploit dev tip of the day: If you want to do JOP on ARM, take a look at the "scatterload" function. Allows you to call arbitrary functions with arbitrary arguments. In a loop. A pretty powerful and a rather generic primitive that I didn't see mentioned anywhere else.
Mar 1, 2023

-
💬 "But he added that the US still lacks a clear consensus as to what happened". A comment that will be overlooked in the rush to say lab-based is the most likely scenario. bbc.co.uk/news/world-us-…
Mar 1, 2023
FBI chief Christopher Wray says China lab leak ‘most likely’
Other US agencies have come to different conclusions from the FBI on how the pandemic began.

I honestly don’t think the Chinese themselves know if COVID came from the lab or not because if it did, everyone who was part of the little fucky wucky would 100% do everything in their power to cover it up and take that shit to the grave.
Mar 1, 2023

-
symbolic execution engine using radare2 backend
Mar 1, 2023

-
⛓️This is a very important industry-wide disclosure since many vendors are affected by the bug in the TPM reference code and specification. "The attacker can also overwrite protected data in the TPM firmware. This may lead to a crash or arbitrary code execution ..." --@fdfalcon
Feb 28, 2023

-
If you come across a bear, never push a slower friend down…even if you feel the friendship has run its course.
Feb 28, 2023

Obviously! You push down the faster friend, they’re the threat. You can already outrun the slow friend.
-
Our story on how unknown parties faked the online identities of two @Reuters reporters @brendagoh_ and @JessiePang0125 to approach activists linked to #China's white paper protests, including @badiucao and those with possible ties to @CitizensDailyCN
Feb 28, 2023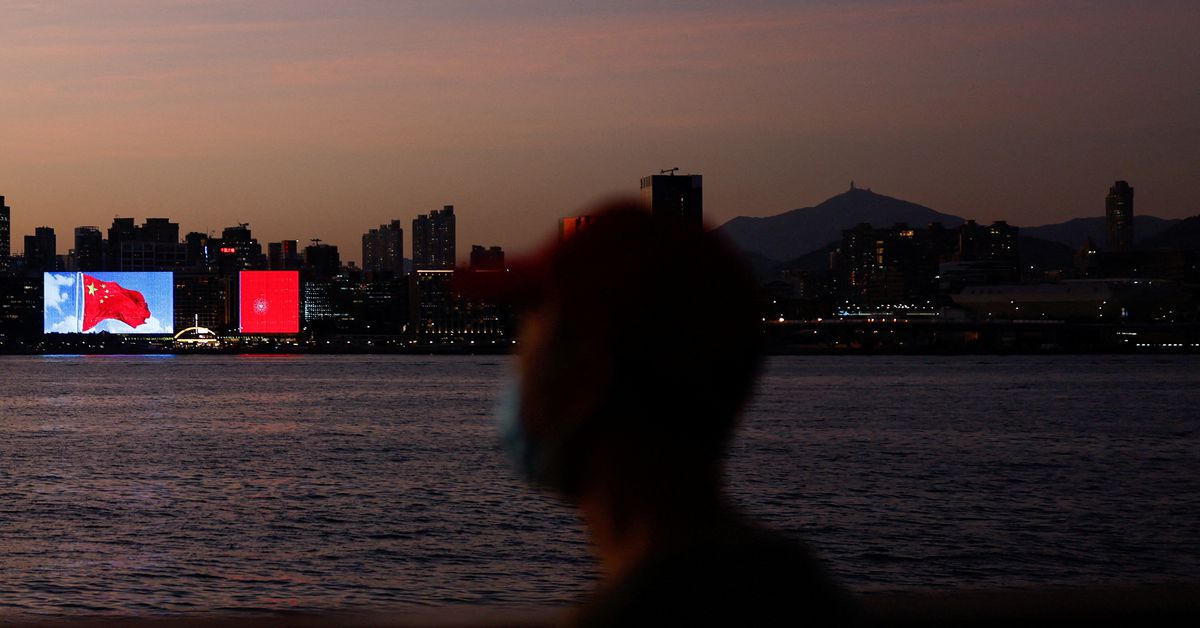
Reuters reporters’ online accounts faked to approach China activists
Two Reuters journalists had their identities faked by an unknown person or people who then used sham social media accounts to engage with Chinese activists on several online platforms over several months.

-
Latest post in my Journalist and Spy series is about Richard Sorge, a German journalist and Soviet intelligence officer active before and during WW II. An expert on Chinese agriculture, but perhaps most known for his espionage networks in China and Japan.
Feb 27, 2023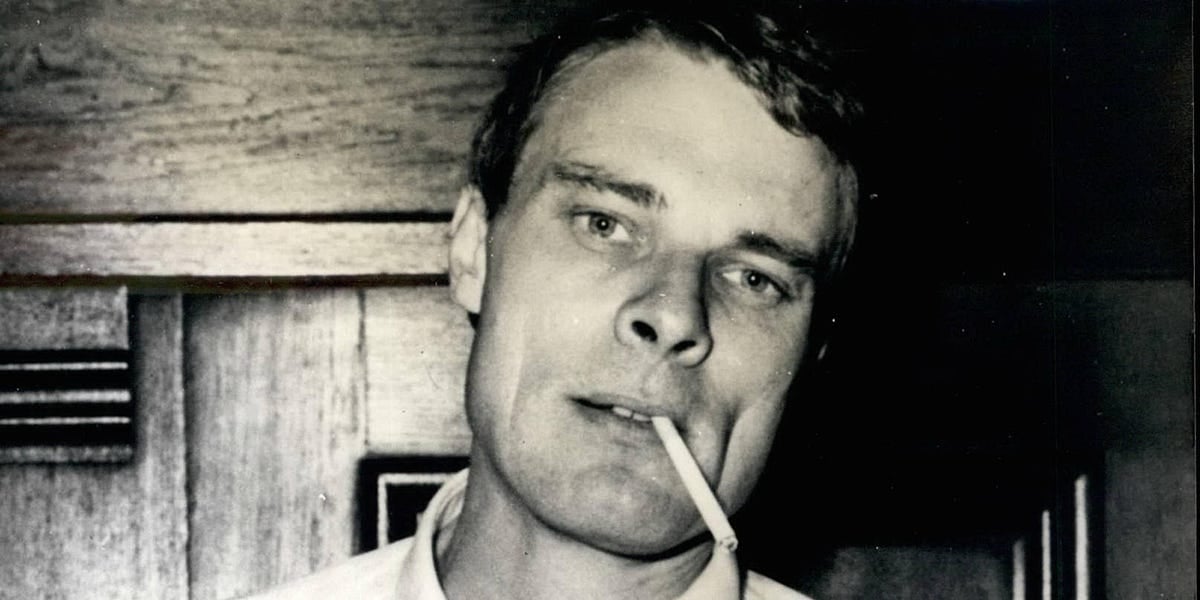
Richard Sorge
Richard Sorge was a German journalist and Soviet intelligence officer active before and during World War II. Sorge visited Scandinavia and the U.S. at various times in his career, though he’s perhaps most known for his work in China and Japan. While there, Sorge established himself as an expert on C…

-
This company called @Microsoft runs this package manager called @nuget. They host a curl package there, that was last updated in 2013 and now contains **68** documented vulnerabilities. But there is apparently no way I can report this or make them act on this.
Feb 28, 2023

-
Microsoft's new Kosmos-1 is incredible. It's a new Multimodal Large Language Model (MLLM). Their model can understand images, text, images with text, OCR, image captioning, visual QA. It can even solve IQ tests. Paper: arxiv.org/abs/2302.14045 Code: github.com/microsoft/unilm
Feb 28, 2023


Add a comment: