June 27, 2022
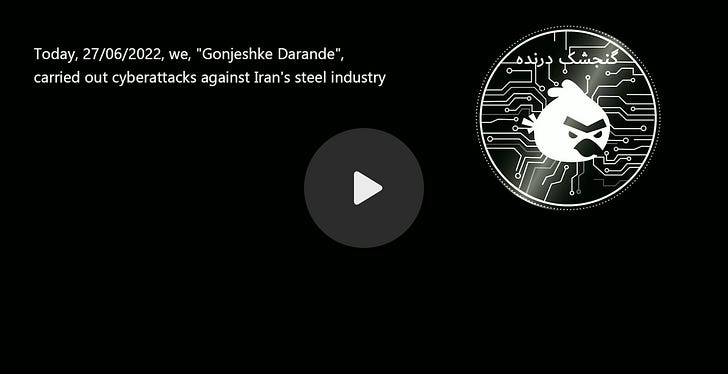
Some “hacktivists” *cough* *cough* have trashed steel works in Iran. Their justification is ridiculous — “these plants are sanctioned” which they claim makes them legitimate targets for attack. Now, I’m not saying they arent legitimate targets, but I am saying that being sanctioned does not automatically equate to being a legitimate target.
What I really want to talk about though, is the level of effort that the operators took to make sure that the attack didn’t harm people. Not only did they take pains to ensure this, but they also made it a pillar of their announcement, along with proof that they took those steps.
This team wanted to make clear what they believe responsible offensive cyber looks like. And they have. I think this is how norms will be created, not in academic or policy papers.
Speaking of academic papers, lets look at another issue — cyberwar. Some have argued that for cyberwar to be a thing, humans lives must be taken. That there must be violence, the body must be damaged, for a cyber attack to be “real war.”
Now, personally, I dont think that is true, but I want to bring up a more interesting point — one aspect of the value of cyber is the ability to minimise harm to people while still achieving objectives.

The best coverage is, of course, from @hkashfi
@juanandres_gs @ChicagoCyber The attacked factory had confirmed the incident in an official announcement and they have closed the production line until further notice. Their demo video also shows interesting artifacts, including outdated PRTG monitoring software.
Jun 27, 2022

As mentioned by Hamid, it looks like the access vector was IRISA, a service and infrastructure provider for the entire Iranian steel industry.
در تصویر دیگری که از سوی هکرها منتشر شده، پنل نرمافزاری متعلق به شرکت ایریسا رو میشه دید که این شرکت در حوزه اتوماسیون صنعتی فعالیت میکنه و مهمتر اینکه خدمات شبکه و زیرساخت صنعتی ارائه میده! بنابراین، بعید نیست خود این شرکت، یکی از سرمنشاءهای دسترسی هکرها بوده باشه.
Jun 27, 2022

If you want some background on the threat actor, I got you fam

Balancing on the rail – considering responsibility and restraint in the July 2021 Iran railways incident – Offensive Cyber Working Group
JD Work [1], [2] An intrusion against a railway network, resulting in destructive effects leading to disruption of cargo and passenger transportation, would in previous decades likely have been con…
-
Enjoy some real hacktivists, or I guess they’ve been promoted to whitehat hackers. Cyber Partisans
-
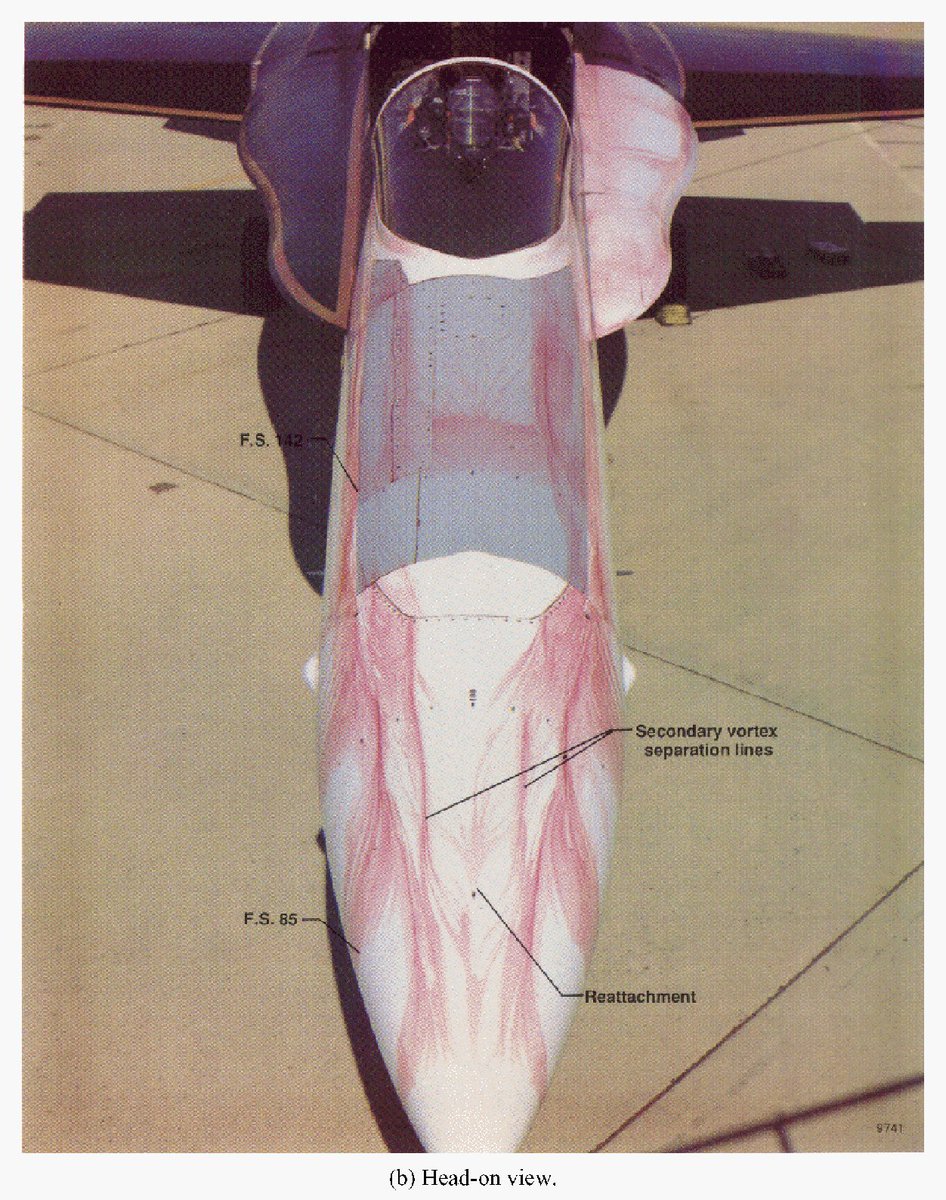
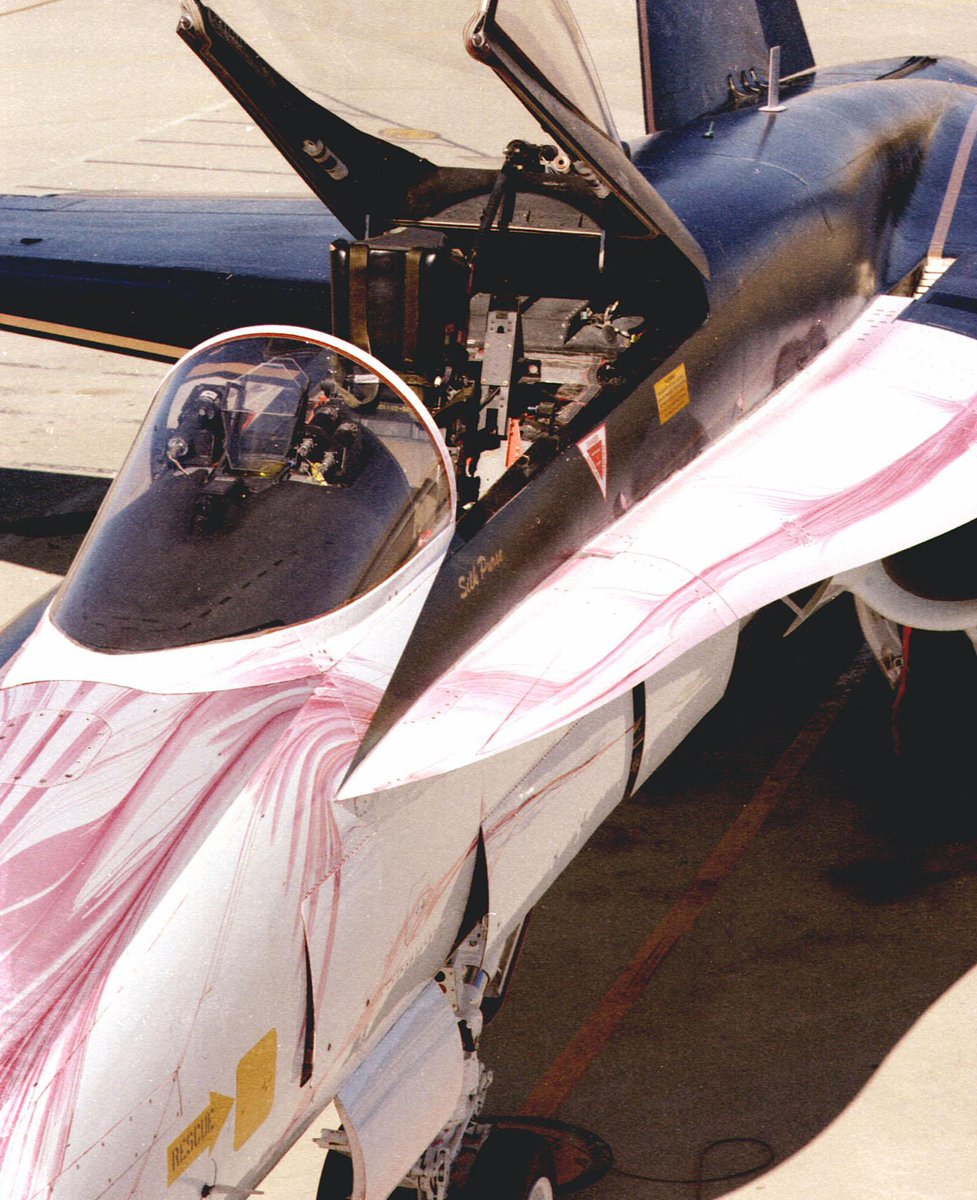
NASA drilled tiny holes around the F-18 High Angle-of-Attack Research Vehicle(HARV) and a red colored glycol-based liquid was released through them in-flight, providing flow visualization for studies
Jun 26, 2022

-


Courtesy of En Nagy, here is the correct Latin:
lurcamus laeti nos debellaturos
-
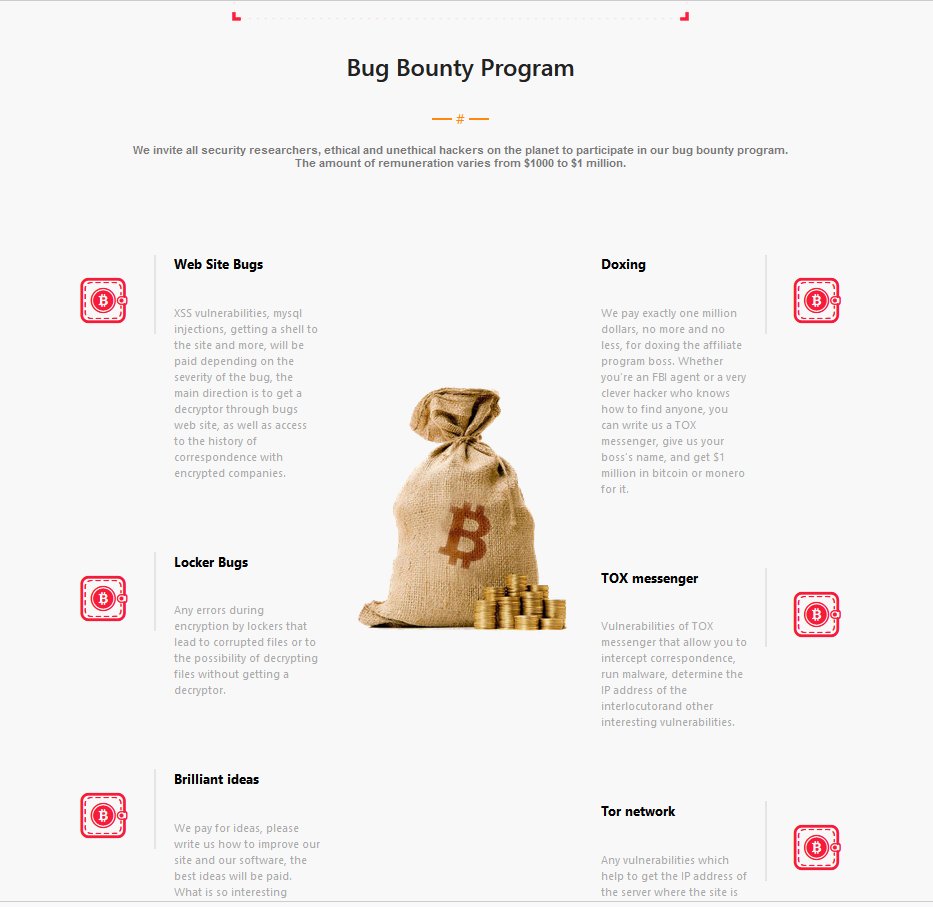
Lockbit ransomware group announced today Lockbit 3.0 is officially released with the message: "Make Ransomware Great Again!" Additionally, Lockbit has launched their own Bug Bounty program paying for PII on high-profile individuals, web security exploits, and more...
Jun 26, 2022

-
New .pdf's from Danish intel oversight. Annual reports 2021: - Centre for CyberSec. (CFCS) tet.dk/wp-content/upl… - Defence Intel Service (FE) tet.dk/wp-content/upl… - Security & Intel Service (PET) tet.dk/wp-content/upl… + Standards for oversight
https://www.tet.dk/wp-content/uploads/2022/06/TET_Standarder2022_english.pdf Jun 27, 2022

-
On 5th May 1945, in the dying embers of the war in Europe, U-534 was caught on the surface by two RAF Liberators in succession. In water too shallow to allow a crash dive the submarine was forced to fight it out.
Jun 26, 2022

-
The year: 2035 Today, your smart toilet sent you a text: "Urinalysis shows you are pregnant. Congratulations. Your mobility status has been updated. You will not be permitted to leave the state until this life is born."
May 6, 2022

-
Don't piss in my mug and tell me it's Coors because I honestly cannot tell the difference.
Jun 26, 2022

-

-
“Syniverse has notified all affected customers of this unauthorized access where contractually required” Call me a loon but maybe, just maybe, we need to better regulate how such breaches are reported and not the cloak and dagger, where contractually required approach used today
Jun 27, 2022

-
The fix for this introduced a (probably remote?) memory corruption bug in the latest OpenSSL release. github.com/openssl/openss…
Jun 22, 2022

-
"Our proposed approach can generate coherent, novel, complex and harmonious symphony compared to human composition + is the pioneer solution for multi-track multi-instrument symbolic music generation." 📄arxiv.org/abs/2205.05448 👩💻 symphonynet.github.io 💻github.com/symphonynet/Sy…
Jun 27, 2022

-

-
Interesting finding in this new @IntelNatSecJnl piece: The UK used its covert Arabic radio station, Sawt Al Saahil, not to spread certain messages, but to reduce the number of people listening to hostile broadcasters by playing light entertainment etc
Jun 27, 2022
Britain’s key counter-subversion instrument before the 1971 withdrawal from the Gulf: Voice of the Coast [Sawt Al Saahil] Arabic radio station
Countering nationalistic, pan-Arabic and anti-British subversion became a core British security policy in the Middle East in the 1950s but Britain only became concerned with subversion in its prote...

-
Imagine: you’ve moved in with your partner. They’re making coffee in the morning while you’re taking a dump in the perspex shitting cube in the middle of your kitchen.
Jun 26, 2022


Add a comment: