December 20, 2022
This video of cops in Nevada searching a suspect and finding a seed phrase is pretty wild. Imagine having your seed phrase become part of public record due to it being captured by an officer's body camera!
Dec 18, 2022

-
-
POC for the new injection technique, abusing windows fork API to evade EDRs.
https://www.blackhat.com/eu-22/briefings/schedule/index.html#dirty-vanity-a-new-approach-to-code-injection--edr-bypass-28417
https://github.com/deepinstinct/Dirty-Vanity
Astra Kernel :verified:: "POC for the new injection technique, abusing wind…" - Infosec Exchange
POC for the new injection technique, abusing windows fork API to evade EDRs. https://www.blackhat.com/eu-22/briefings/schedule/index.html#dirty-vanity-a-new-approach-to-code-injection--edr-bypass-28417 https://github.com/deepinstinct/Dirty-Vanity #infosec #threatintel #threathunting #edr #redteam
-
GreyNoise has released a "Year of Mass Exploits" retrospective report for 2022 highlighting four of the most significant vulnerabilities of the year.
The list includes the Log4Shell (CVE-2021-44228) vulnerability, targeted in nearly one million exploitation attempts within the first week after its discovery.

2022: A Look Back On A Year Of Mass Exploitation
Researchers at GreyNoise Intelligence have added over 230 tags since January 1, 2022, which include detections for over 160 CVEs. In today’s release of the GreyNoise Intelligence 2022 "Year of Mass Exploits" retrospective report, we showcase four of 2022's most pernicious and pwnable vulnerabilities.
Sergiu Gatlan: "GreyNoise has released a "Year of Mass Exploits" …" - Mastodon.social
Attached: 1 image GreyNoise has released a "Year of Mass Exploits" retrospective report for 2022 highlighting four of the most significant vulnerabilities of the year. The list includes the Log4Shell (CVE-2021-44228) vulnerability, targeted in nearly one million exploitation attempts within the first week after its discovery. https://www.greynoise.io/blog/2022-a-look-back-on-a-year-of-mass-exploitation
-
New Mandiant report today assesses with moderate confidence that the GRU directed the pro-Russian "hacktivist" DDoS attack on Mississippi's Secretary of State, keeping it offline most of election day. I expect this to be a huge concern come 2024.
Dec 19, 2022
Information Operations Targeting 2022 U.S. Midterm Elections Include Trolling, Narratives Surrounding Specific Races, Politicians | Mandiant
Mandiant identified information operations activity from various foreign state-aligned campaigns during the 2022 U.S. midterm elections.

-
My power’s really low, so this may be the last image I can send. Don’t worry about me though: my time here has been both productive and serene. If I can keep talking to my mission team, I will – but I’ll be signing off here soon. Thanks for staying with me.
Dec 19, 2022

-
Cryogenic horror stories
https://bigthink.com/the-future/cryonics-horror-stories/-
This holiday season I will be in good spirits as long as good spirits are in me.
Dec 19, 2022

-
"It is often impossible to work out exactly where private risk ends and public risk starts" - why Govts are getting increasingly involved in cyber security Pt 2 of my series of articles on the two data breaches in Australia is now available on Substack!
Dec 20, 2022
Lessons from Down Under’s Data Disasters, Pt 2
Many of the problems in cyber security are economic and social, not technical. And digitisation privatises public risk like never before. That’s why Governments are increasingly required to step in

-
I swore I'd get this out before Twitter went up in a fireball. So here it is: THE MUSICAL STRUCTURE OF GEOMETRIC ELAMITE do you like mysterious undeciphered tablets? do you like maybe the literally oldest music in existence? boy do I have the PDF for you academia.edu/93268214/Music…
Dec 19, 2022

-
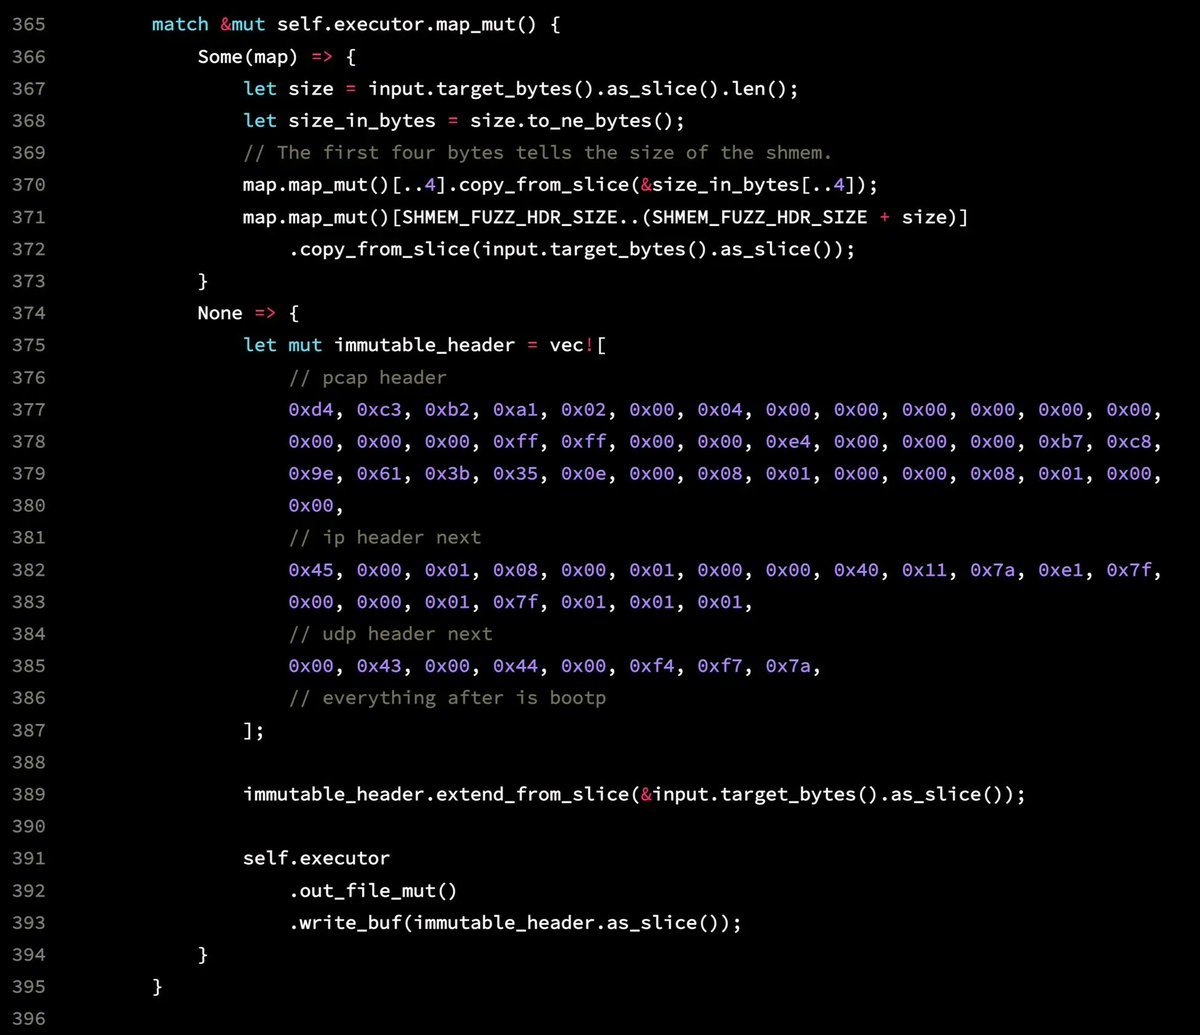
Cool series about fuzzing and LibAFL (credits @epi052) 1: epi052.gitlab.io/notes-to-self/… 1.5: epi052.gitlab.io/notes-to-self/… 2: epi052.gitlab.io/notes-to-self/… 3: epi052.gitlab.io/notes-to-self/… 4: epi052.gitlab.io/notes-to-self/… 5: epi052.gitlab.io/notes-to-self/… #fuzzing #libafl #infosec #learning
Dec 19, 2022

-
Wizards guide to debugging
The Pocket Guide to Debugging
-
This is very much the strategy of the United States, clearly laid out. https://t.co/O1UWwuEzDB
Dec 20, 2022

Remarkable how matter-of-fact offensive cyber operations have become. Normalizing fast. In this case, disruptions across borders to preempt a hypothetical action in the future U.S. targeted adversary cyber infrastructure to safeguard midterm vote
Dec 20, 2022
U.S. targeted adversary cyber infrastructure to safeguard midterm vote
The U.S. military’s Cyber Command hunted down foreign adversaries overseas ahead of this year’s mid-term elections, taking down their infrastructure before they could strike, the head of U.S. Cyber Command said.

-

Add a comment: