August 5, 2022
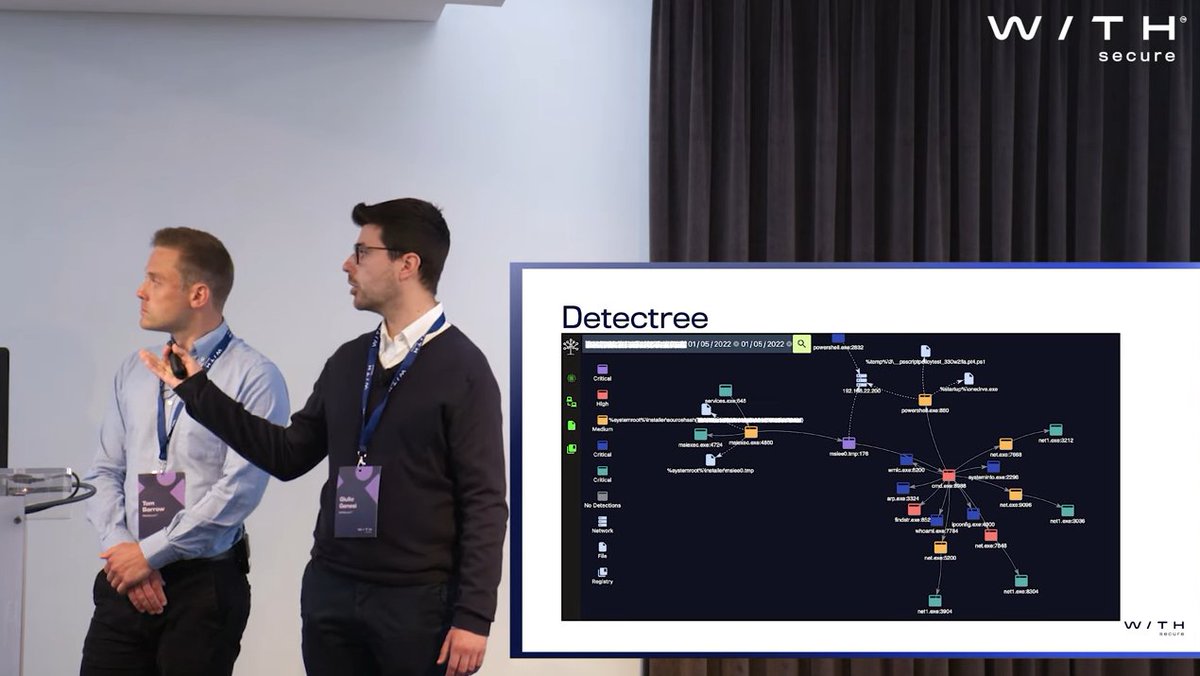
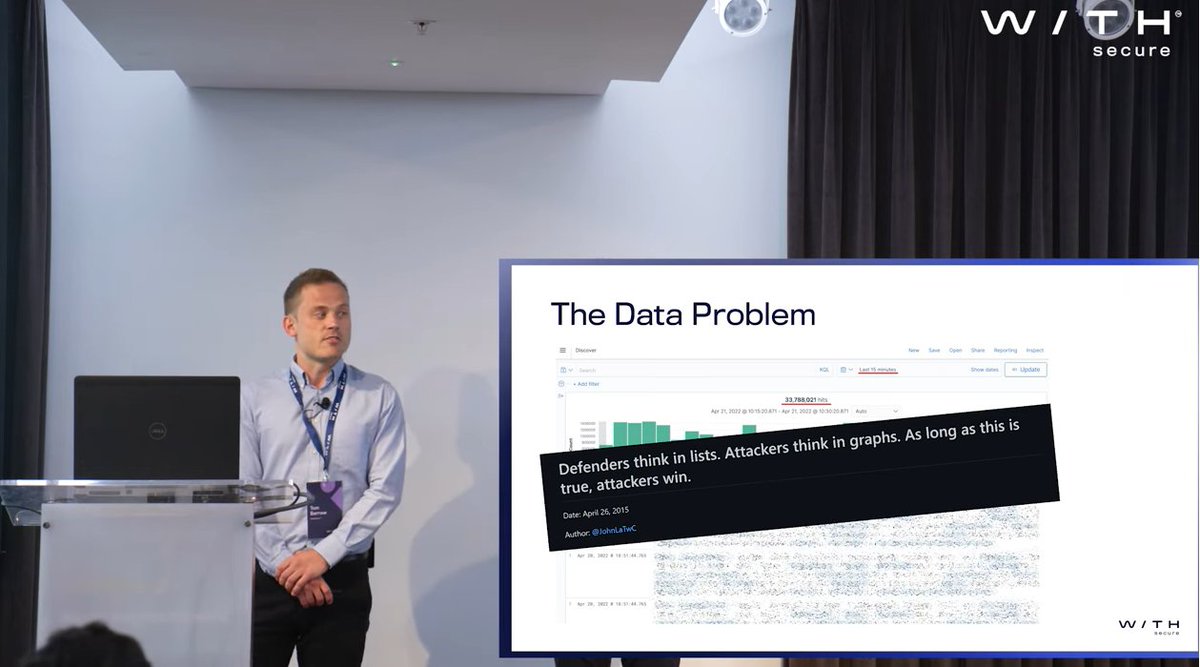
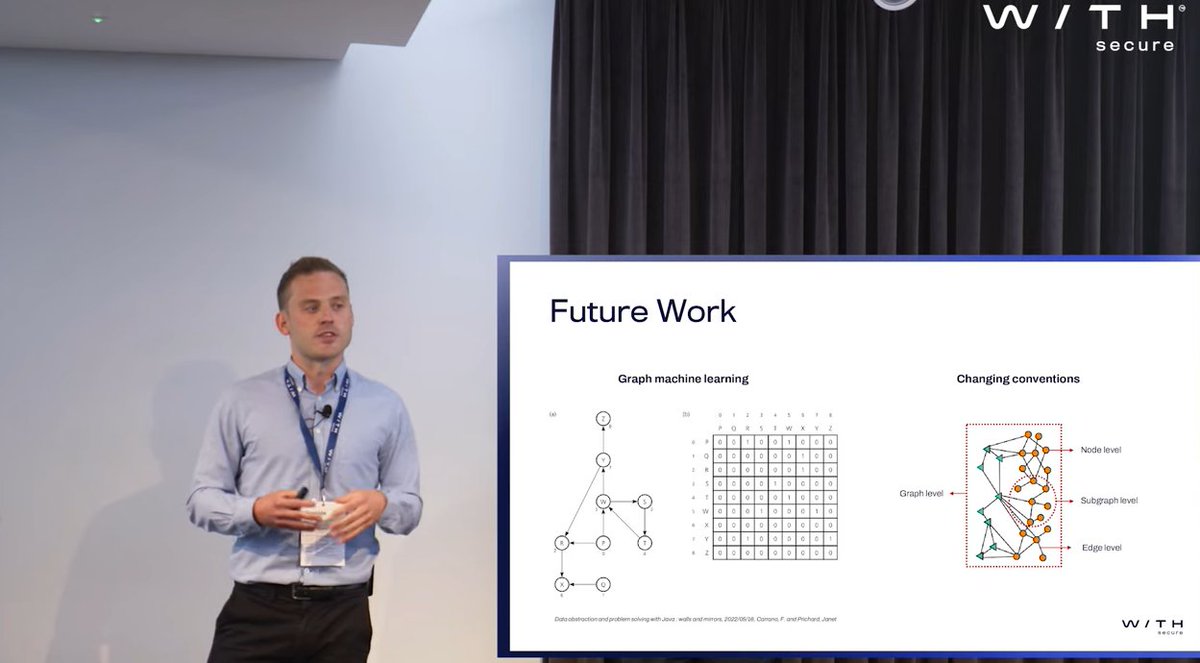
ICYMI, if graph visualization and investigation together pique your interest, watch this talk by Tom @AnduinSwim & Giulio @Blazef104 of @WithSecure on Detectree. It began life as a @Jupyter Notebook! 📺youtube.com/watch?v=EBVhGs… 🕹️labs.withsecure.com/tools/detectree 🔗github.com/countercept/de…
Jul 31, 2022

-
Outstanding work by our information operations team, which continues to expose Chinese IO. This time they’ve linked a PR firm to the activity. This crew fabricated a letter from Senator Rubio and has turned their attention to Taiwan issues lately.
Aug 4, 2022
Pro-PRC “HaiEnergy” Information Operations Campaign Leverages Infrastructure from Public Relations Firm to Disseminate Content on Inauthentic News Sites | Mandiant
New pro-PRC IO campaign that’s disseminating content on inauthentic news sites and fabricating content to discredit critics of the Chinese Government.

-
Want to find bugs faster? Let me teach you a cool trick to help!
Aug 4, 2022
Find bugs faster with the command line
In this video I will teach you how to find bugs faster using command line tools. Using zipgrep we will find some hard coded credentials in jar files.If you w...

-
BREAKING: Mandiant is attributing the ransomware attack that took down Albanian government networks and cut off public services in mid-July to Iranian actors. Albania is a NATO member. This is an escalation from previous focus on Middle East targets. 1/x
Aug 4, 2022
Likely Iranian Threat Actor Conducts Politically Motivated Disruptive Activity Against Albanian Government Organizations | Mandiant
Mandiant attributes the ransomware attack against the Albanian government network in July of 2022 to an Iranian threat actor.

⚠️ Confirmed: #Albania's National Agency for Information Society (AKSHI) network has been temporarily shut down to counter a major cyberattack; real-time network data show service cut for hours beginning Saturday night, impacting online government services 📉
Jul 17, 2022

Hat Tip to @gossithedog
-


-
👀 “An investigation into seven different apps on the Mac App Store, including the number one PDF reader in the U.S., has found that all of them are orchestrated by the same Chinese developer using fake reviews and command-and-control exploits to try and target users.” https://t.co/kkrXG0zN7g
Aug 4, 2022

-
SCOOP We got our hands on screen shots of an early prototype of Pegasus, called Syaphan and intended for use by the Israeli police These photos are the closest we’ve gotten to seeing real working Pegasus system THREAD @JoshBreiner @haaretzcom haaretz.com/israel-news/20…
Aug 4, 2022

-
1/ We just released our Q2 Adversarial Threat Report. Highlights: 2 South Asian cyber-espionage ops, deep dive into a RU troll farm engaging around Ukraine, Philippines elections, and Emerging Harms cases from Greece, India, South Africa, and Indonesia 🧵 about.fb.com/news/2022/08/m…
Aug 4, 2022
Meta’s Adversarial Threat Report, Second Quarter 2022 | Meta
We’re sharing insights into the threats we see worldwide and covert influence operations that we tackle.

-
People should be required to spend 2 years’ worth of their weekends cosplaying pointless “presence patrols” and meetings with unfriendly police chiefs and village councils before they are allowed to cosplay busting into people’s homes and killing them in their beds https://t.co/M6vJP2mhWr
Aug 4, 2022

-
I was applying for homeowners insurance today and they asked if I had any pets to which I said, “yes, two cats.” And then they asked me “have they been trained to attack or cause bodily harm?” and I wanted to know if anyone had been able to do this because I’ll hire you
Aug 3, 2022

-
We have a new report out analyzing a suspended Facebook and Instagram network linked to an Israeli digital marketing firm. A lot of effort went into the part of the network that posted about Palestinian politics.
Aug 4, 2022

-
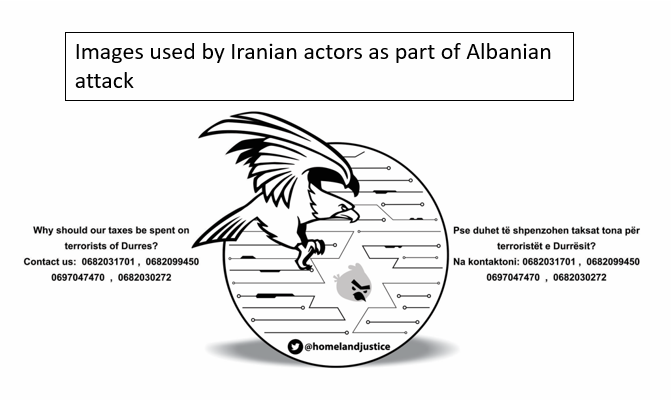
Posing as Albanian nationalists, the Iranian actor leaked government docs and railed against the MeK. Check out the imagery. Notice the Angry Bird in the Star of David? When Iranian steel was targeted in a cyber op, a group called Predatory Sparrow used an Angry Bird logo. 3/x
Aug 4, 2022

-
If you’re using a Silicon Graphics workstation running their “IRIX” operating system, and you launch the Audio control panel with a “-spinaltap” flag on the executable, all the volume sliders go to 11 🎶🤣🎶 #RetroComputing #RetroGaming
Aug 4, 2022

-
Such a nifty trick! ADS-B reports position uncertainty, so if you map the uncertainty, you can map the GPS jamming.
Aug 5, 2022
-
If you haven't gone through @enisa_eu 2022 Threat Landscape for #Ransomware Attack, here are a few good reasons to explore this new publication. enisa.europa.eu/publications/e… Follow me on in this exiting 🧵 [1/6]
Aug 3, 2022
ENISA Threat Landscape for Ransomware Attacks
This report aims to bring new insights into the reality of ransomware incidents through mapping and studying ransomware incidents from May 2021 to June 2022. Based on the findings, ransomware has adapted and evolved, becoming more efficient and causing more devastating attacks.

-
Apple shows more indications it plans to conflate privacy & confidentiality, getting into local ad targeting, having your (their?) devices rather than their servers profile you (for concerns about the targeting, what’s the difference?). my thoughts here: netzpolitik.org/2022/future-of…
Aug 4, 2022

-
A 🧵 about cyber insurance, and some myth-busting on some topics that I read this week. Full disclosure: I work for a cyberinsurance provider and will only talk about how WE are doing things,we too agree the it could be done better and decided to do it.1/N
Aug 4, 2022

-
“a concentrate of abnormalities, coincidences, and improbabilities bordering on the impossible”

Body Double - JSTOR Daily
Long before the imposture of Anna Delvey, the Tichborne Claimaint swept a nation’s imagination.
-
Read the whole thing and the best assessment is at the bottom:
Said one U.S. official, speaking on condition of anonymity because of the matter’s sensitivity: **“The burning of the access was immaterial because if access is easy to achieve and regain, then burning it brings a minimal cost.”**
-
Part 3 of the "A journey into IoT" series is out! Topic: reversing of unknown radio signals. I tried to write these articles with many details, in order to make them as clear as possible also to security researchers approaching hardware for the first times
Aug 5, 2022
A journey into IoT - Unknown Chinese alarm - Part 3 - Radio communications - hn security
Disclaimer: as many other security researchers […]

-
A new ransomware strain named Gwisin has been spotted in targeted attacks against South Korean companies asec.ahnlab.com/en/37483/
Aug 5, 2022

-
As macro malware is dying out, LNK builders are all in the rage again sentinelone.com/labs/who-needs…


Aug 5, 2022

-
What a cool interactive map! Type in an English word and the website translates into all European languages. Hours of fun. It knows swear words too - just sayin'... Source: buff.ly/2QIxFjd
Aug 4, 2022

-
🚨Scoop: From autumn, migrants will be required to scan their faces on smartwatches up to five times a day. In May the @ukhomeoffice awarded tech co @wearebuddi a £6m contract to produce facial recognition watches, which will track location 24/7. theguardian.com/politics/2022/…
Aug 5, 2022
Facial recognition smartwatches to be used to monitor foreign offenders in UK
Home Office and MoJ plans will require migrants convicted of crimes to take photos up to five times a day

-
The correct answer (from a developer) to “did you accidentally copy a password hash into a URL” should be: “how the heck would I ever access the user’s password hash even if I wanted to?” And yes I realize this is wishful thinking.
Aug 5, 2022

-
At least a million CCTV cameras supplied by a Chinese state-owned company are installed in the UK. Channel 4 News can reveal the government has turned down a request to meet the company amid security concerns, with reports of some cameras trying to connect to Chinese servers.
Aug 3, 2022


Add a comment: