August 12, 2022
There are some cool projects these days to provide more private access to mobile phone networks.
The pretty good phone privacy project has just entered public beta.
PGPP
About PGPP
There was an earlier pseudonymous sim project before.
@thegrugq @_Sn0rkY reminds me of the osmocom imsi pseudpnymization project we released some years ago:
Aug 12, 2022
Wiki - IMSI Pseudonymization - Open Source Mobile Communications
Redmine

There is a Russian SIM offering which seems to be a very similar implementation (an MVNO) with a different type of protection. In this case the security is from the silence of the MVNO, rather than the MVNO being unable to link the IMSI in use to a particular customer.
https://www.unlimitedsecuredevices.com/product-collection/encrypted-russian-mvno-sim-server-pgp-multi-imsi-server-
We have released another exploit from the archives (2008), SharpSeatbelt, abusing a vulnerability in the Scheme interpreter embedded in Apple Mac OS X's Seatbelt policy compiler: subreption.com/offensive-secu… Includes a novel trick against Scheme interpreters!
Aug 10, 2022
Subreption - SharpSeatbelt: Stack-based Buffer Overflow Exploit for the Mac OS X Seatbelt policy compiler
-

-
If anybody is wondering why Cisco are disclosing, the threat actors appear to have forced their hands. I doubt Cisco were able to whip up that blog post in an hour on a whim 🤣
Aug 11, 2022

-
AI tools that write generic blog posts and massage the content to be SEO friendly are already starting to flood Google search results. This is a case of HOOTL (human out of the loop) information warfare!
-
Slides of my #BHUSA2022 talk about "A Journey Into Fuzzing WebAssembly Virtual Machines" are already available here! If you want to learn different fuzzing techniques and the processes around them, this talk might be useful!
https://fuzzinglabs.com/wp-content/uploads/2022/08/BHUSA22_fuzzing_webassembly_vm_patrick_ventuzelo.pdf Aug 11, 2022

-
Kim Zetter, of Kim Zetter’s newsletter fame, gave a keynote at BlackHat on part of the cyber warfare part of the Russia Ukraine war. In particular the IT Army and what it means for the future of cyber conflict. Things like, “is it ok to allow attacks to originate in your state against another state?” And, “what do the IT Army do after the war is over?”
Topics we’ve covered on ‘The Kim Zetter’s Newsletter Glasshouse Cyber Hour Show’

Russian invasion has destabilized cyber security norms
The inside scoop on the Ukrainian IT army, and what could happen next
Also relevant is the paper by Stefan Soesanto which she cites
It's out: The first detailed write-up on "The IT Army of Ukraine - Structure, Tasking, and Ecosystem." You'll get insights into the IT Army's targeting flow and coordination, the non-public structure, where Ukraine's intel services are, and much more. css.ethz.ch/content/dam/et…
Jun 22, 2022

-
We caught another zero-day in the wild (CVE-2022-37042)! This time it was an authentication bypass that was used to facilitate remote code execution via CVE-2022-27925 on Zimbra mail servers around the world. Check out the @Volexity blog on it!
Aug 11, 2022
Mass Exploitation of (Un)authenticated Zimbra RCE: CVE-2022-27925
[Note: Volexity has reported all findings in this post to Zimbra. Where an existing contact was known, Volexity has notified local CERTs of compromised Zimbra instances in their constituency. The newest versions of Zimbra are patched for both the RCE vulnerability and authentication bypass vulnerabi…

-
The DogWalk exploit for CVE 2022 34713 patched this last Tuesday.
microsoft-edge + ms-search + MSDT path traversal 0day = fun of 2-clicks (one click additional due to Protected View if docx is coming from remote btw).
Jun 6, 2022

-
Nice! FTC is looking to crackdown on data collection and online surveillance
https://www.ftc.gov/news-events/news/press-releases/2022/08/ftc-explores-rules-cracking-down-commercial-surveillance-lax-data-security-practices-
The evolution of the internet: Web 1.0: static content Web 2.0: dynamic user generated content Web 3.0: scams
Aug 11, 2022

-
Being a straight woman is wild because you have to date your only natural predator.
Jun 25, 2022

-
The world excel esport championship is on espn.
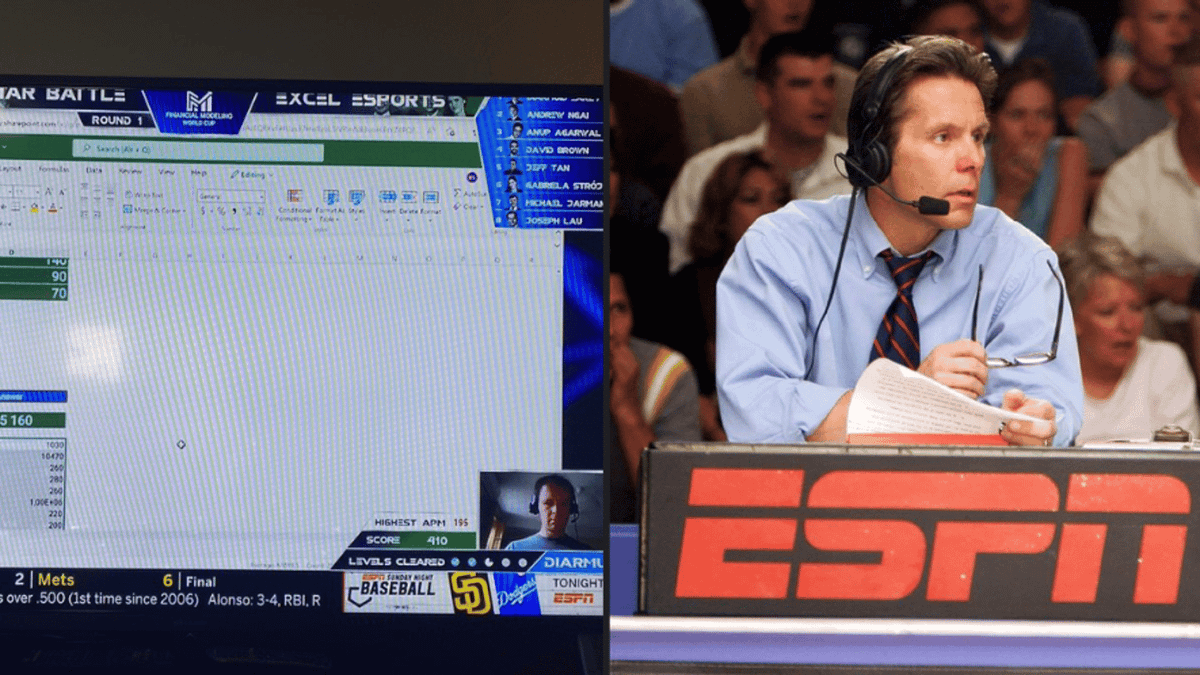
The World Excel Championship is being broadcast on ESPN and it's absolutely wild
The sport pits eight expert modellers against each other. There's commentators, thrills, spills and a lot of exciting moments.
-
When the science reporter is on holiday but the food reporter is working https://t.co/PqpKbkxCyK
Aug 11, 2022

-
The CDC has relaxed its advice on quarantining after being bitten, as most people are already zombies anyway
Aug 11, 2022

-
ClipboardInject - Abusing the clipboard to inject code into remote processes This PoC uses the clipboard to copy a payload into a remote process, eliminating the need for VirtualAllocEx / WriteProcessMemory. x86matthew.com/view_post?id=c…
Aug 10, 2022

-
Bookmarking isn't about reading something later, it's about not reading it now
Aug 11, 2022

-
Everybody wants the client to fund their private counterintelligence investigation cosplay... ... nobody wants to do an asset inventory.
Aug 12, 2022

-
Trump has to be one of the first cast members of Home Alone 2 to sell stolen nuclear secrets to the Saudis for $2 billion
Aug 12, 2022

-
Shot:
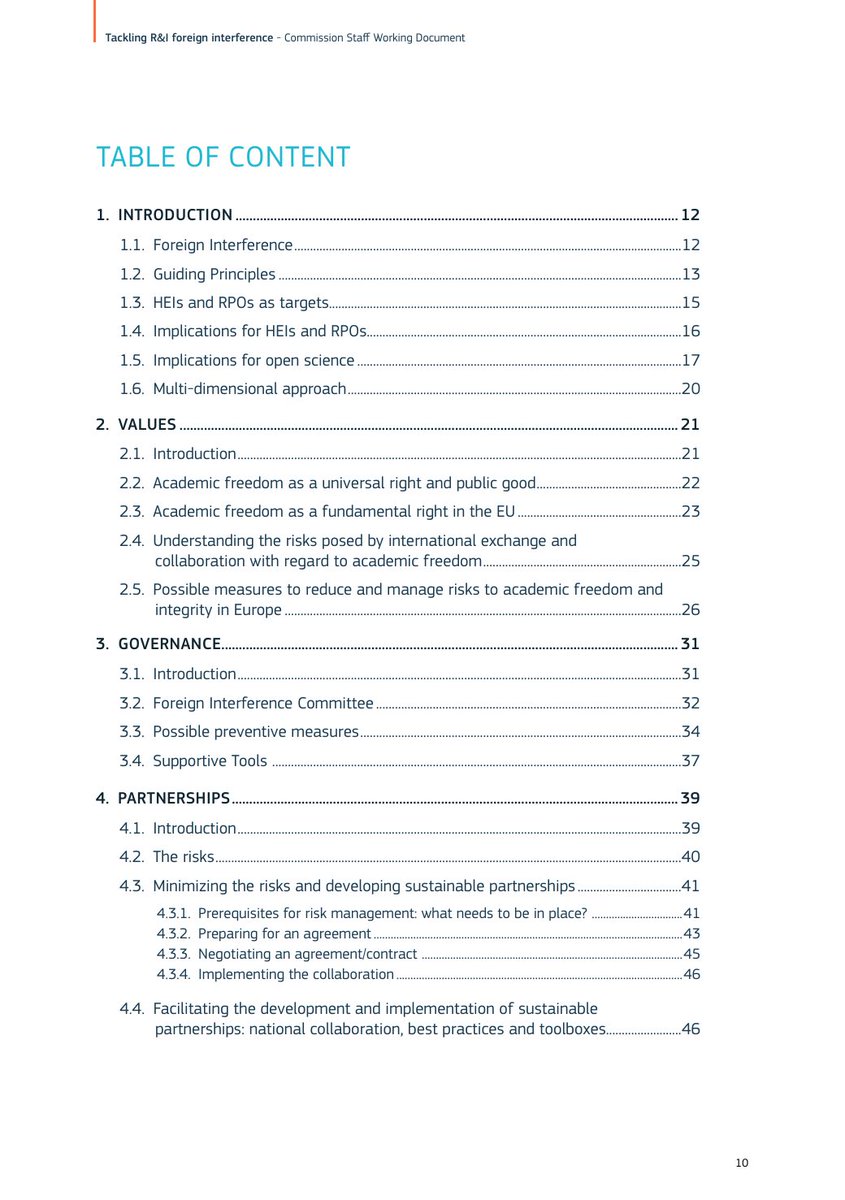
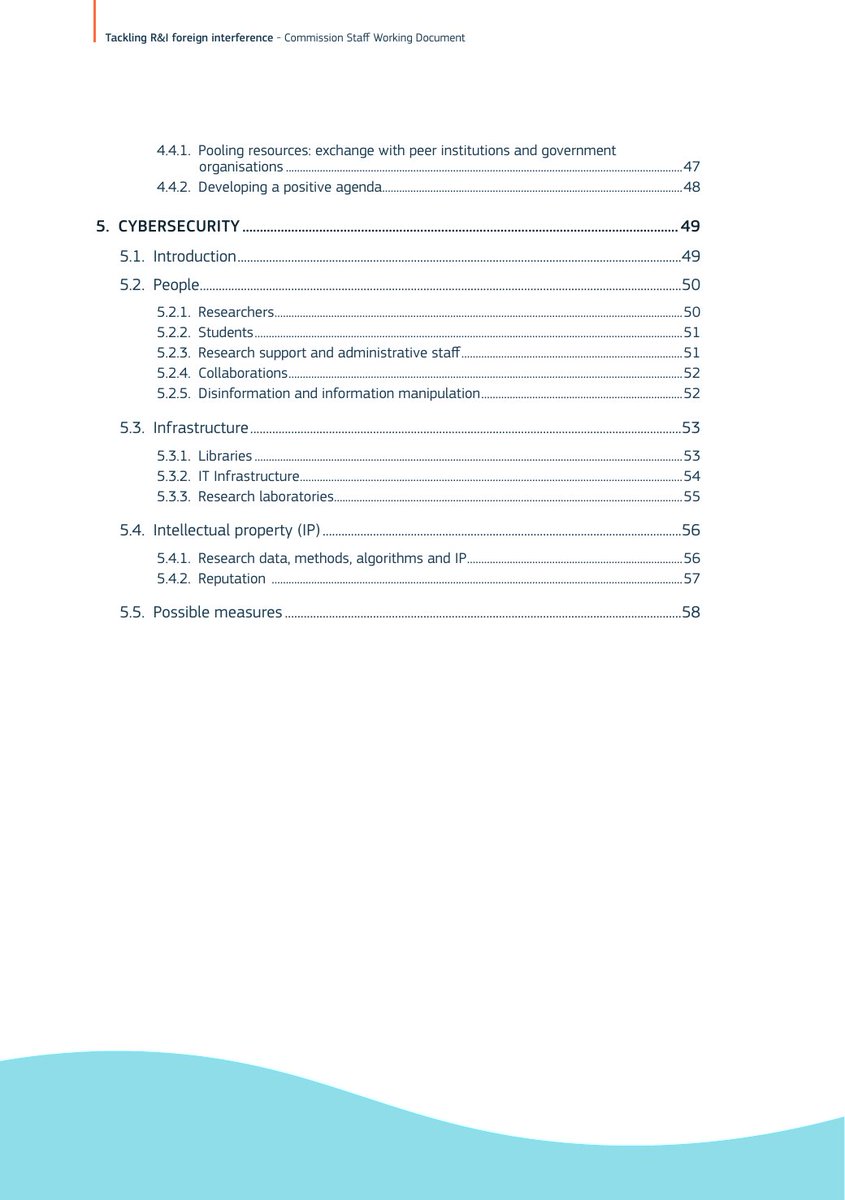
EU Commission staff working doc on foreign interference in higher education and R&D orgs: Tackling research & innovation (R&I) foreign interference (0.5MB .pdf, Jan 2022, 63 pages) op.europa.eu/o/opportal-ser… Areas of attention grouped in values, governance, partnerships & infosec.
Aug 10, 2022

Chaser:
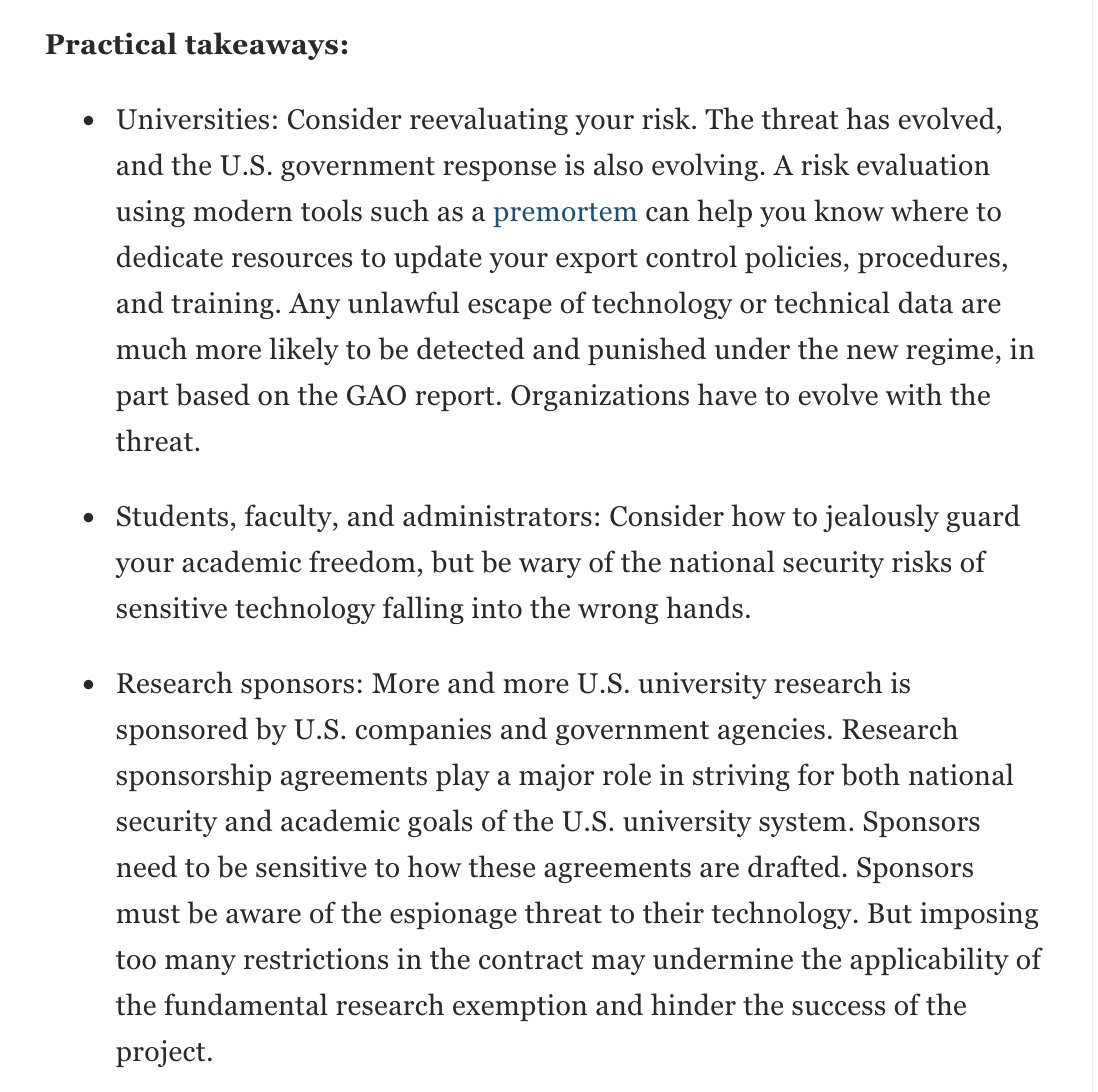
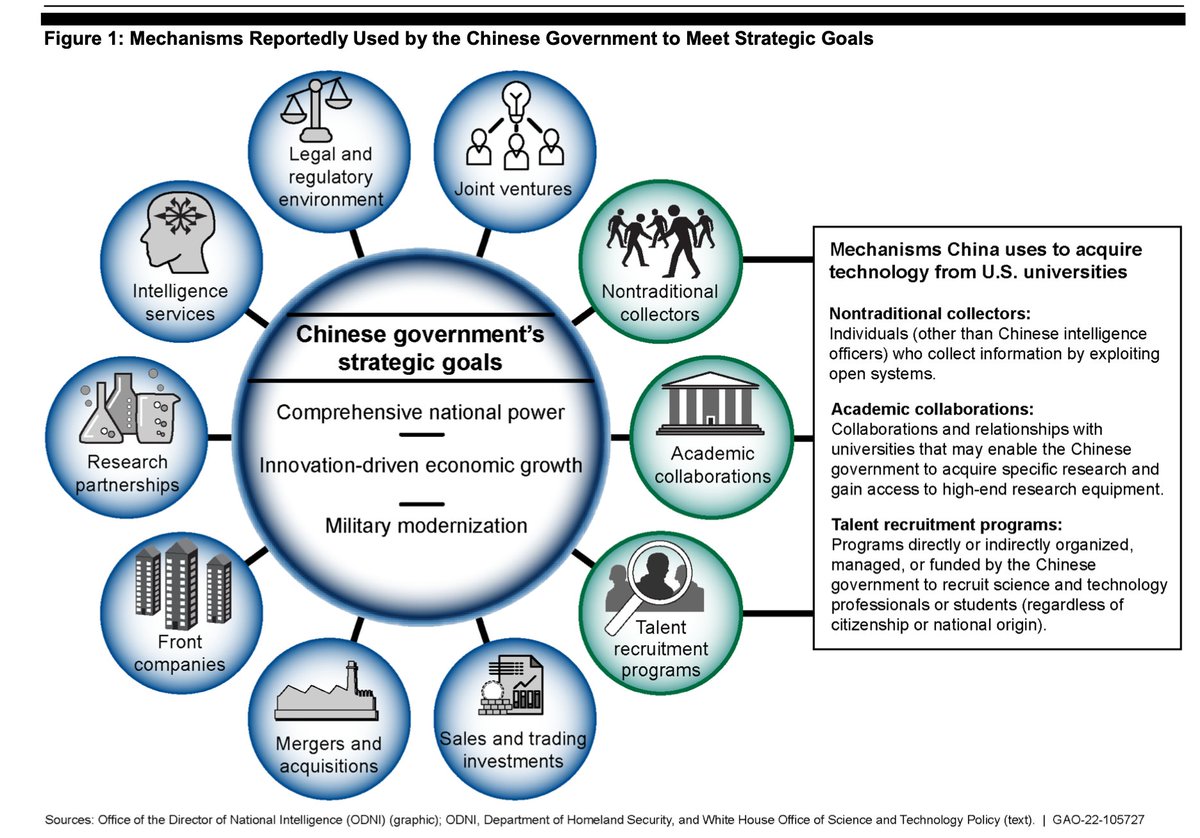
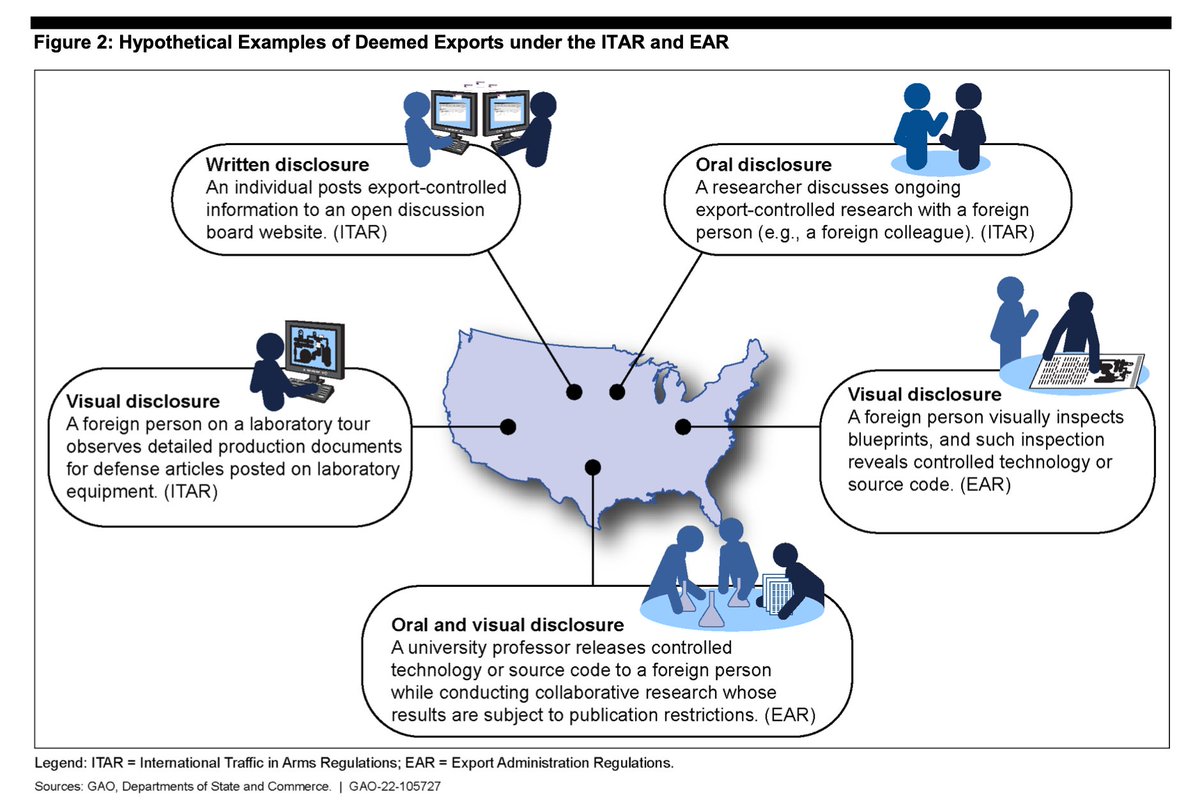
U.S. perspective on risks of foreign espionage (interference) to higher education and R&D: U.S. Gov't Pursues More Aggressive Action to Curb Espionage at Universities (Aug 10) jdsupra.com/legalnews/u-s-… More: GAO-22-105727 report (5MB .pdf, June 2022, 58p): gao.gov/assets/gao-22-…
Aug 12, 2022


Add a comment: