WordPress Template Break-In
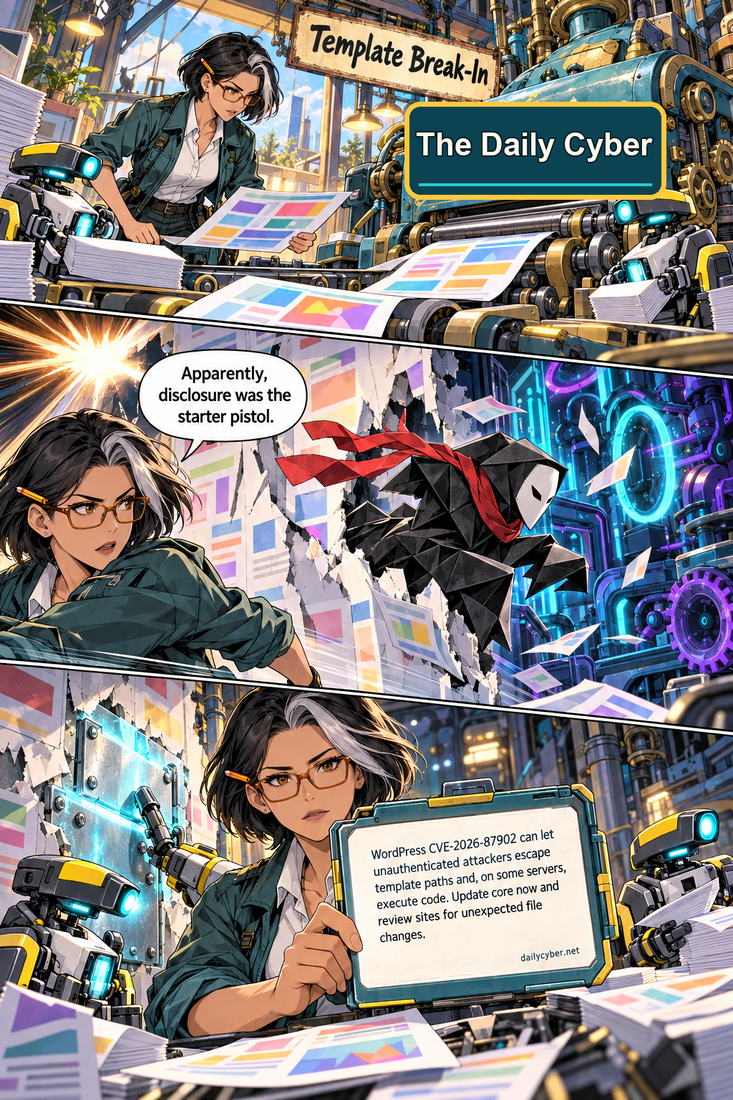
WordPress Template Break-In
Attackers began exploiting WordPress Core flaw CVE-2026-87902 within hours of disclosure; under certain theme and server conditions it can lead to remote code execution. Update to the latest supported release and review sites for unexpected file changes.
Don't miss what's next. Subscribe to The Daily Cyber: